Unpatched OnePlus Vulnerabilities Let Malicious Apps Gain Root Access
 scsecOctober 4, 20262 Mins read5
Unpatched OnePlus Vulnerabilities Let Malicious Apps Gain Root Access
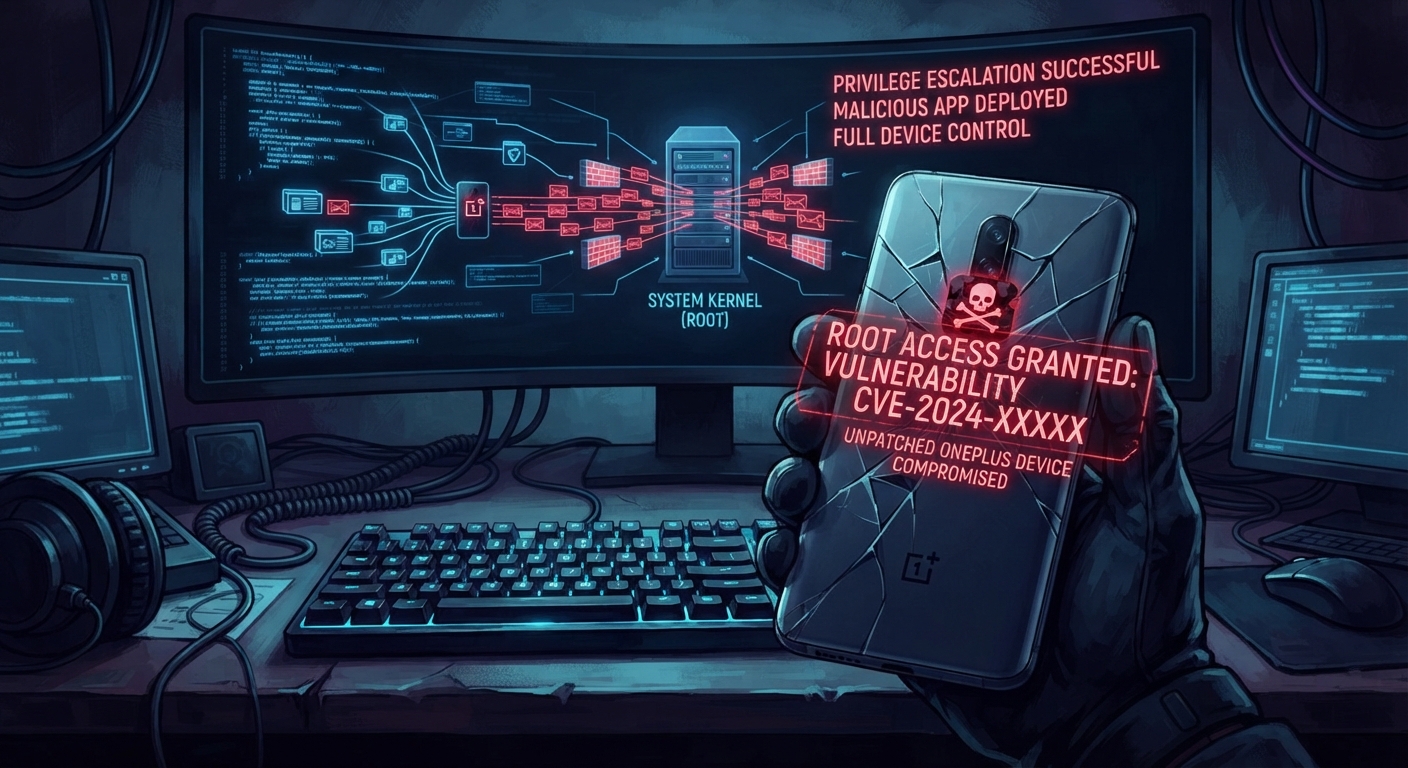
Two unpatched vulnerabilities in OnePlus software could allow a malicious Android application to gain root-level control of an affected smartphone without requesting any special permissions.
Security researcher Rasmus Moorats demonstrated the attack on a OnePlus 15 running the latest version of OxygenOS. He was able to chain the two vulnerabilities together to move from an ordinary application to complete system-level control.
OnePlus confirmed the vulnerabilities in May and indicated that many additional OnePlus and OPPO devices could potentially be affected. However, the company has not publicly provided a complete list of affected models.
The first vulnerability exists in a OnePlus service called AtlasService.
AtlasService collects debugging information and operates with root privileges. The service accepts requests from applications without properly verifying which application is making the request.
A malicious application can send specially crafted input to the service. That input eventually reaches a debugging component that passes it into a system command without sufficient validation.
This gives the malicious application root privileges, although initially within a restricted environment known as the dumpstate security domain.
The second vulnerability allows the attacker to escape that restriction.
It affects another OnePlus component called olc2, a hardware-related service capable of executing shell commands. The service assumes that the caller is already root and therefore does not provide adequate protection against the attacker who has obtained root through the first vulnerability.
By chaining the two bugs together, the attacker can execute commands with much broader Linux privileges.
This level of access can potentially allow the attacker to load kernel code and gain extensive control over the smartphone.
The attack is not remotely exploitable by itself. A malicious application must first be installed on the device.
However, the researcher demonstrated that the malicious application does not need to request special permissions. It can therefore potentially operate without triggering the normal permission warnings users expect from dangerous applications.
There is currently no evidence that the vulnerabilities have been used in real-world attacks.
Moorats reported both vulnerabilities to OnePlus on April 18, 2026. OnePlus confirmed them in May and said a fix was being planned. The researcher later published his findings on September 24 after receiving no further response to his requests for updates.
At the time of publication, OnePlus had not released a security update specifically addressing the vulnerabilities, and no CVE identifiers had been assigned.
Moorats also demonstrated the attack on an older OnePlus 12 Pro and believes the vulnerabilities may affect a wider range of devices running OxygenOS 16.
Because OnePlus and OPPO share significant elements of their software platforms, OPPO devices may also be affected.
Until patches become available, the most practical protection is to avoid installing applications from untrusted sources. Since the attack requires a malicious application to be installed first, restricting software installations can significantly reduce the risk.
Related Articles
Pentagon Personnel Database Breach Exposes Sensitive Data of Millions
Pentagon Personnel Database Breach Exposes Sensitive Data of Millions The U.S. Department...
Critical cPanel Vulnerability Lets Hosting Accounts Execute Code as Root
Critical cPanel Vulnerability Lets Hosting Accounts Execute Code as Root A newly...
North Korean Cyber Campaign Compromises 30,000 Devices Through Fake Job Interviews
North Korean Cyber Campaign Compromises 30,000 Devices Through Fake Job Interviews A...


Fake LastPass Installers Used to Deploy Rapuncel Stealer and Disable Security Software
Fake LastPass Installers Used to Deploy Rapuncel Stealer and Disable Security Software...

Leave a comment