South Korea Probes Bank Breaches Amid Suspected AI-Powered Cyberattacks
 scsecOctober 8, 20261 Mins read4
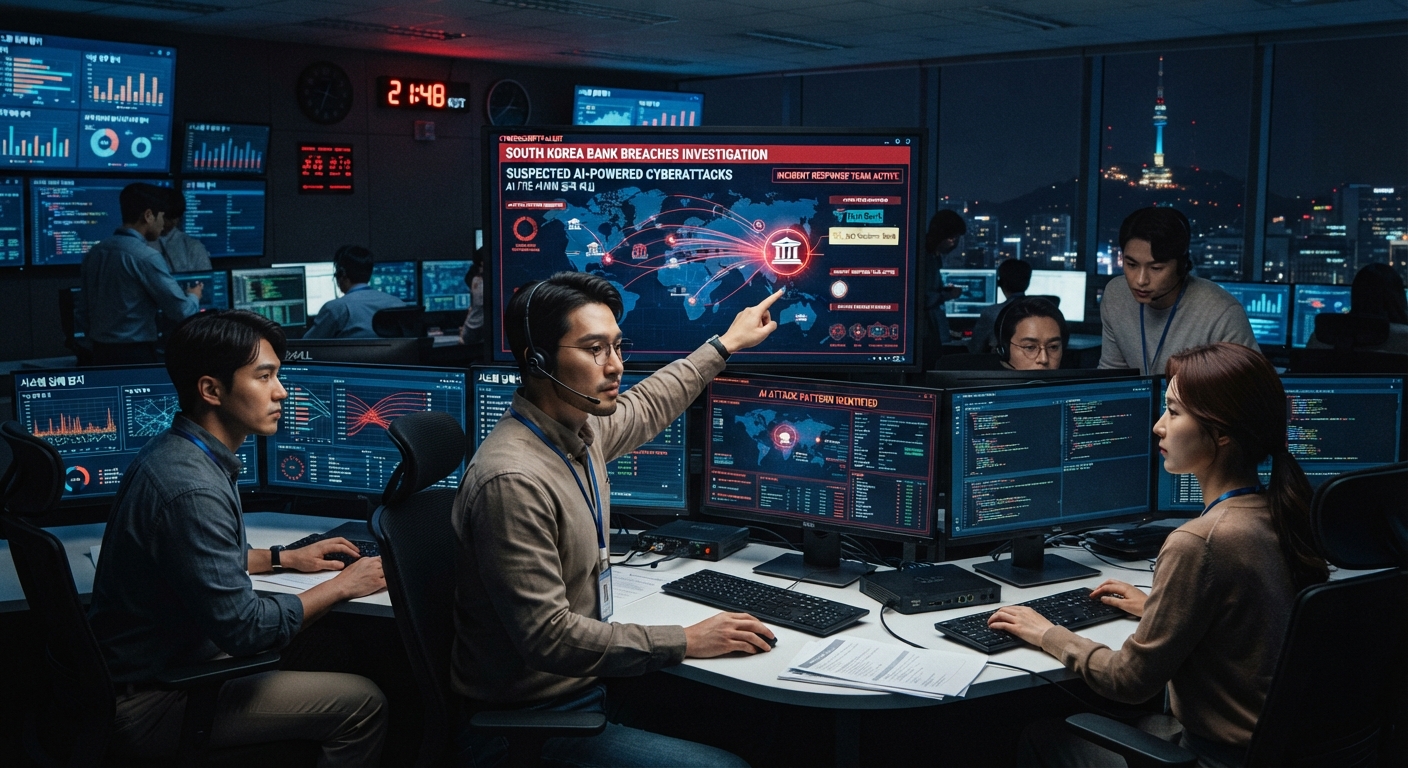
South Korea Investigates Bank Breaches as AI-Powered Hacking Is Suspected
South Korean authorities have launched investigations into a series of cyberattacks affecting major financial institutions, amid growing suspicion that attackers may have used artificial intelligence to automate parts of their operations.
The Financial Services Commission held an emergency meeting after multiple financial companies reported cybersecurity incidents. Officials confirmed a data breach at Shinhan Bank and said other banks, including KB Kookmin Bank, had also experienced security incidents.
Authorities launched on-site investigations and shared information with relevant agencies, including the Korea Internet & Security Agency. Financial institutions have been instructed to review externally accessible systems, including services that are not directly exposed to customers, reduce unnecessary information exposure and strengthen authentication and access controls.
Banks have also been ordered to rapidly share threat intelligence and coordinate their responses while submitting the results of their internal security inspections.
The incidents have raised concerns over the protection of customer information. Reports indicated that Shinhan Bank suffered a breach involving information belonging to about 25,000 customers, while Kookmin Bank reportedly experienced exposure involving credit-card information from 119,000 customers. Hana Bank was also found to have suffered a limited breach after its sales-support system was compromised.
The country’s leadership has ordered a broader investigation into personal-data leaks affecting financial and public institutions.
AI connection under investigation
Investigators are also examining evidence that attackers may have relied on AI-assisted penetration-testing technology.
Local reports said a server involved in the attacks contained an HTML page title featuring a Chinese-language string associated with ARTEX AI, an open-source penetration-testing platform capable of automating tasks such as information gathering, vulnerability discovery, attack-path planning, security-tool execution and vulnerability verification.
However, South Korean banks and financial authorities have not confirmed that ARTEX AI was used during the attacks. The presence of the Chinese-language string also does not establish who was responsible for the breaches.
Security experts have nevertheless suggested that AI-based attack automation could have played a role. If confirmed, the incidents would demonstrate how automated security tools can potentially accelerate the discovery and exploitation of weaknesses across financial networks.
Authorities are continuing to investigate the breaches while reviewing whether existing cybersecurity controls and regulatory requirements need to be strengthened.
Related Articles
Hackers Hijack Domains After Breaching Country-Code Registries and Obtain Rogue Certificates
Hackers Hijack Google-Related Domains After Compromising ccTLD Operators Hackers have hijacked domains...
Ransomware Hacker Betrays His Own Gang to Keep Extortion Profits
Ransomware Affiliate Turns on His Own Gang to Keep Ransom Payments A...
ClingSTUN Linux Backdoor Exploits Dozens of Vulnerabilities to Spread Across
Linux Backdoor ClingSTUN Uses STUN Protocol to Spread Across Vulnerable Devices A...


Pentagon Personnel Database Breach Exposes Sensitive Data of Millions
Pentagon Personnel Database Breach Exposes Sensitive Data of Millions The U.S. Department...

Leave a comment