ClingSTUN Linux Backdoor Exploits Dozens of Vulnerabilities to Spread Across
 scsecOctober 8, 20261 Mins read4
Linux Backdoor ClingSTUN Uses STUN Protocol to Spread Across Vulnerable Devices
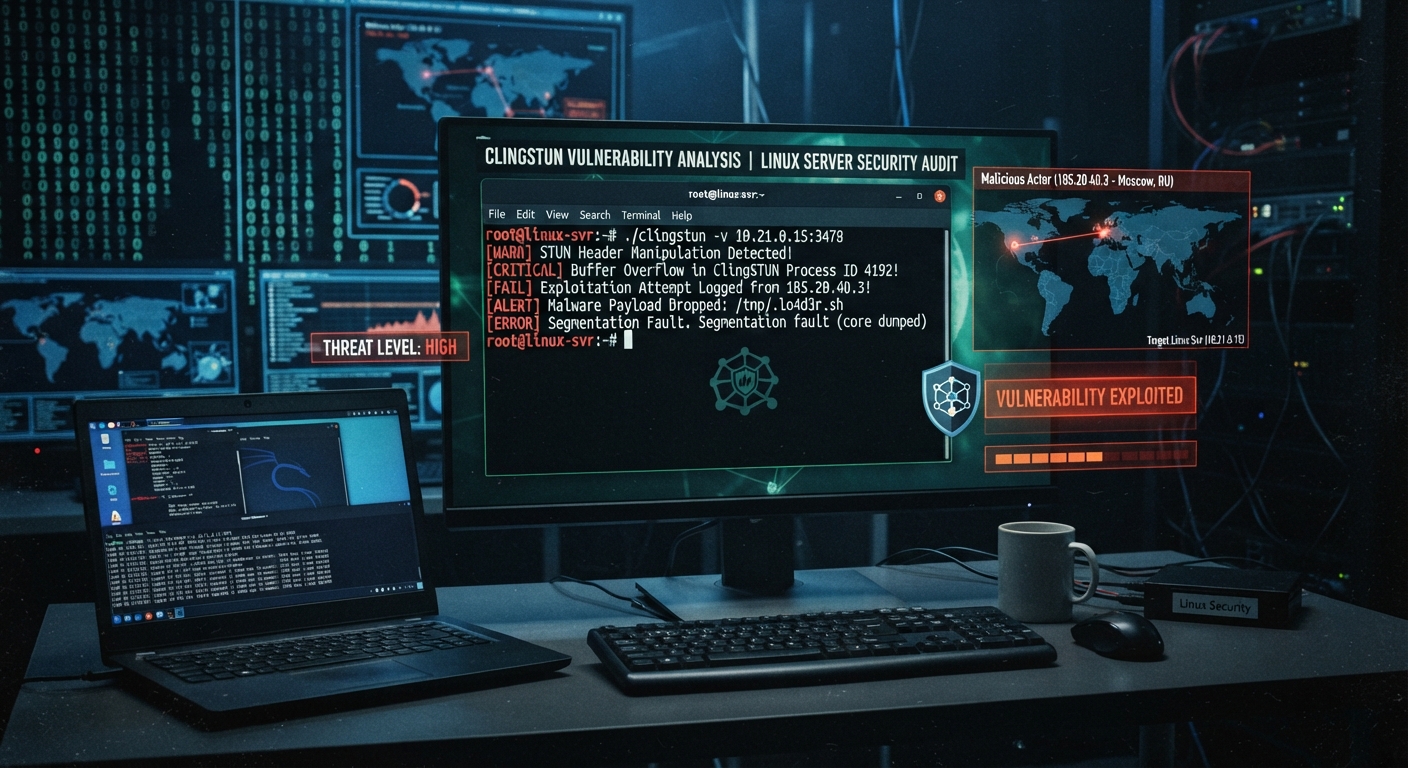
A newly identified Linux backdoor called ClingSTUN is turning compromised systems into back-connect proxies while using the legitimate STUN networking protocol to maintain connectivity. Security researchers say the malware is equipped with exploits for dozens of vulnerabilities and can spread itself to additional devices.
According to FortiGuard Labs, ClingSTUN targets around two dozen vulnerabilities affecting products from vendors including Avtech, EnGenius, D-Link, Hytec, Ivanti, Lantronix, Linear, MeiG, Realtek, Sunhillo, Tenda and TP-Link. Researchers also found a self-propagation component containing hardcoded exploits for seven vulnerabilities affecting products from China Mobile, KGUARD, Linksys, LB-LINK, MVPower, Realtek and TBK.
The malware can download payloads designed for several processor architectures, including AMD x86-64, ARM, Intel 80386, MIPS and PowerPC, allowing the operators to target a broad range of Linux-based equipment.
ClingSTUN also attempts to maintain access after a system is compromised. It copies itself into hidden executable files and modifies multiple system initialization scripts so that it can restart when the machine boots.
Researchers observed several versions of the malware carrying out similar activities, including terminating competing processes, disabling watchdog mechanisms, establishing persistence and accepting remote commands.
One of the malware’s most unusual characteristics is its use of public STUN servers. ClingSTUN creates a UDP connection and sends STUN binding requests to determine external IP addresses and port mappings. It then periodically sends information such as its group identifier and mapped ports back through the same STUN endpoints.
This approach can help the malware maintain connectivity through NAT environments without relying on a conventional command-and-control registration path.
The backdoor can also monitor specially crafted packets that allow its operators to execute commands remotely and initiate further propagation.
FortiGuard Labs cautions that legitimate STUN servers should not automatically be treated as malicious infrastructure because they are publicly available services. Instead, defenders should look for STUN activity occurring alongside unusual processes, unexpected UDP connections and repeated keepalive traffic.
The discovery highlights how attackers are increasingly combining large vulnerability portfolios with legitimate internet services to make malware harder to detect and more capable of surviving inside compromised environments.
Related Articles
Hackers Hijack Domains After Breaching Country-Code Registries and Obtain Rogue Certificates
Hackers Hijack Google-Related Domains After Compromising ccTLD Operators Hackers have hijacked domains...
Ransomware Hacker Betrays His Own Gang to Keep Extortion Profits
Ransomware Affiliate Turns on His Own Gang to Keep Ransom Payments A...
South Korea Probes Bank Breaches Amid Suspected AI-Powered Cyberattacks
South Korea Investigates Bank Breaches as AI-Powered Hacking Is Suspected South Korean...


Pentagon Personnel Database Breach Exposes Sensitive Data of Millions
Pentagon Personnel Database Breach Exposes Sensitive Data of Millions The U.S. Department...

Leave a comment