Hackers Hijack Domains After Breaching Country-Code Registries and Obtain Rogue Certificates
 scsecOctober 8, 20262 Mins read3
Hackers Hijack Google-Related Domains After Compromising ccTLD Operators
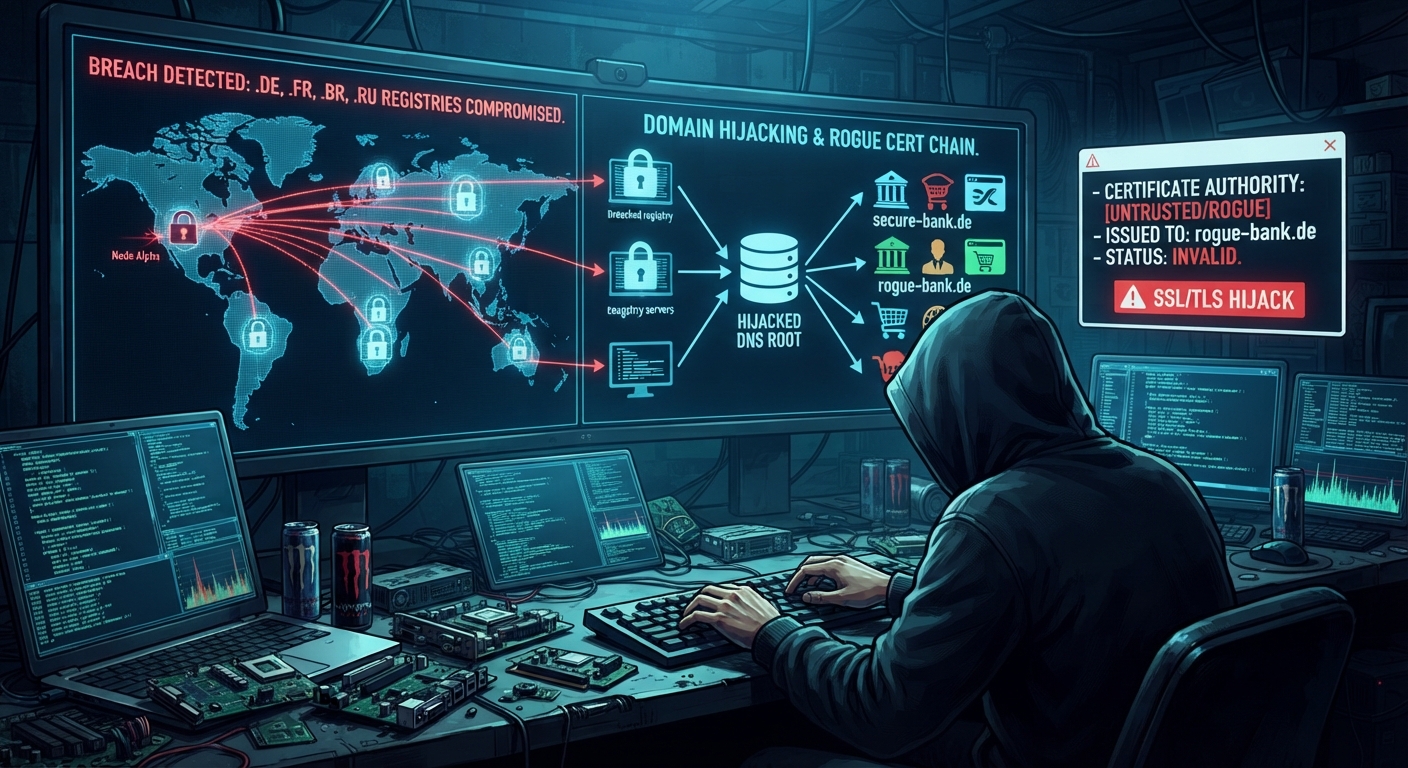
Hackers have hijacked domains under the country-code top-level domains for Ghana, Sierra Leone and American Samoa after compromising third-party operators and altering authoritative DNS records.
The attacks also allowed the threat actors to obtain unauthorized HTTPS certificates for several Google-related domains. Google stressed that its own systems were not compromised.
The attackers reportedly gained access to DNS records associated with the affected .GH, .SL and .AS domains. By changing authoritative DNS records, they were able to redirect domains to infrastructure under their control.
The DNS takeover also created an opportunity to obtain legitimate HTTPS certificates. Certificate Authorities normally verify domain ownership before issuing certificates, and one common validation method requires the requester to create a specific DNS TXT record.
With control over the DNS records, attackers could satisfy that verification requirement and obtain valid certificates for domains they did not actually own.
This created a serious impersonation risk because compromised domains could be used to serve arbitrary content while appearing to have legitimate HTTPS protection.
Google responded by blocking unauthorized certificates associated with its properties through Chrome’s CRLSets, an emergency mechanism that allows the browser to quickly block revoked or untrusted certificates. Google also worked with certificate issuers to revoke the certificates.
The company subsequently examined Certificate Transparency logs and identified additional certificates that appeared connected to the campaign. Several other major organizations and widely used online services were believed to have been affected, and Google proactively blocked additional certificates in Chrome.
Google emphasized that the incident did not result from a compromise of its own systems and said there was no indication that the certificate authorities involved acted improperly.
However, the company warned that the full scope of the DNS hijacking may not yet be known. Chrome’s emergency protections also do not automatically protect users of other browsers.
Google has advised domain owners to continuously monitor Certificate Transparency logs across their domain portfolios, including parked domains. It also recommends using restrictive Certification Authority Authorization records where appropriate to control which certificate authorities and validation methods can be used.
CAA records cannot prevent certificate issuance while an attacker actively controls DNS, but they can help prevent additional certificates from being issued using cached validation after legitimate DNS control has been restored.
The attackers have not been publicly identified, and Google has not disclosed the total number of certificates confirmed to have been compromised.
Related Articles
Ransomware Hacker Betrays His Own Gang to Keep Extortion Profits
Ransomware Affiliate Turns on His Own Gang to Keep Ransom Payments A...
South Korea Probes Bank Breaches Amid Suspected AI-Powered Cyberattacks
South Korea Investigates Bank Breaches as AI-Powered Hacking Is Suspected South Korean...
ClingSTUN Linux Backdoor Exploits Dozens of Vulnerabilities to Spread Across
Linux Backdoor ClingSTUN Uses STUN Protocol to Spread Across Vulnerable Devices A...


Pentagon Personnel Database Breach Exposes Sensitive Data of Millions
Pentagon Personnel Database Breach Exposes Sensitive Data of Millions The U.S. Department...

Leave a comment