Ransomware Hacker Betrays His Own Gang to Keep Extortion Profits
 scsecOctober 8, 20262 Mins read4
Ransomware Affiliate Turns on His Own Gang to Keep Ransom Payments
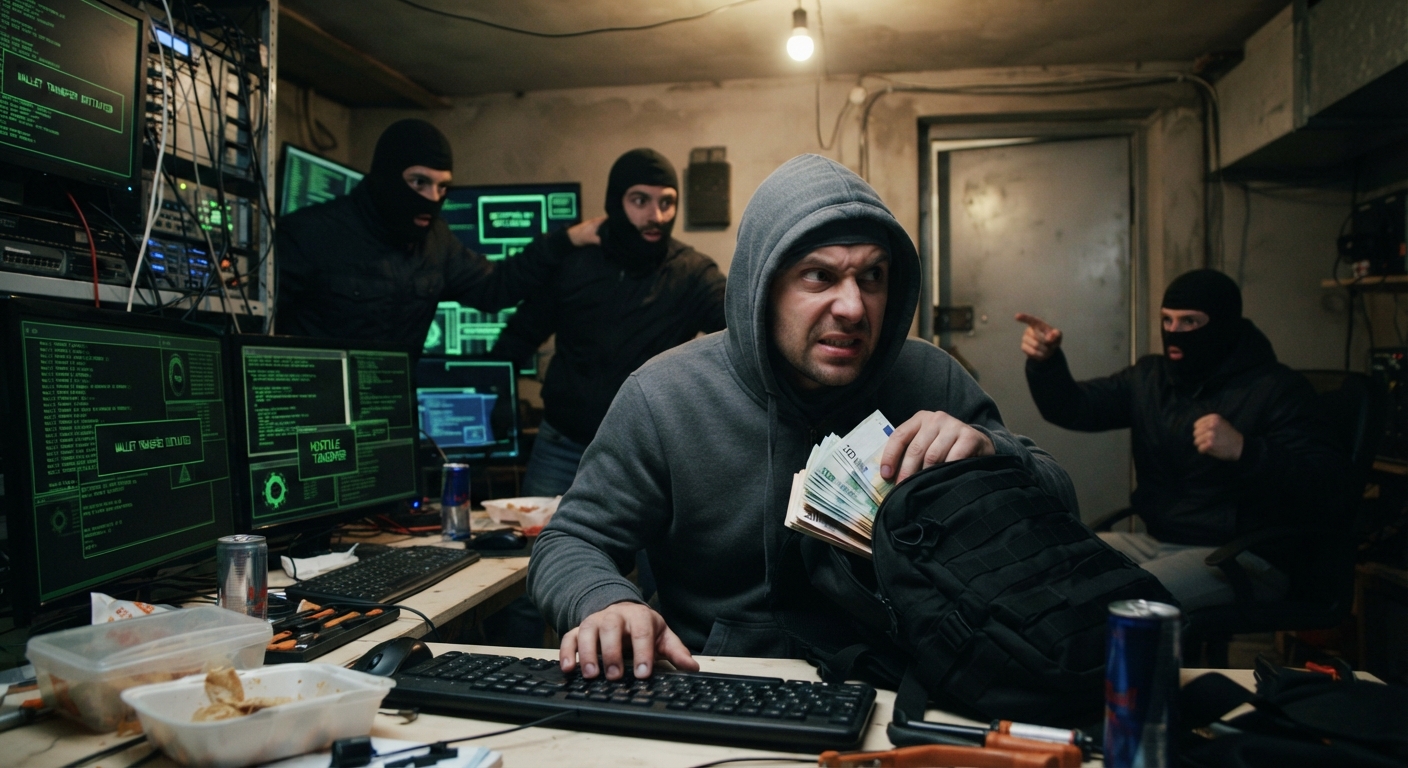
A ransomware hacker known as Azazel allegedly betrayed the criminal group he worked with by creating an independent leak site and collecting extortion payments for himself instead of sharing the proceeds with the ransomware operation.
CloudSEK researchers identified Azazel as a Russian-speaking affiliate of the Gentlemen ransomware group. Using the group’s tools, negotiation channels and ransom-note template, the hacker targeted more than two dozen organizations across six countries.
The victims came from a wide range of sectors, including logistics, healthcare, insurance, pharmaceuticals and government-related services.
The operation was unusually large for a ransomware affiliate. Researchers identified more than 50TB of dedicated infrastructure, including a 22TB storage vault apparently used to retain stolen data and other campaign-related material.
Rather than following the normal ransomware-as-a-service arrangement, Azazel reportedly established an independent leak platform called LEAKNED. Victim data was published there, while ransom and extortion proceeds were allegedly collected directly, bypassing the Gentlemen group’s revenue-sharing structure.
Researchers also found evidence that at least one data theft operation remained active during their investigation, with the amount of stolen data increasing by hundreds of gigabytes between observations.
The attacks were reportedly enabled by stolen CI/CD secrets. A compromised GitLab installation was used against two organizations, while a single exposed CI/CD token provided access to more than 150 databases belonging to a SaaS platform and its customers.
AI enters the criminal operation
The campaign also stands out because of its apparent use of AI tooling.
CloudSEK described the case as an unusual early example of cybercriminals integrating AI agents into their operations. Azazel reportedly registered a reverse shell as a callable tool inside an AI agent through the Model Context Protocol, allowing the criminal to conduct parts of the attack through an AI-driven environment.
The hacker also created infrastructure designed to search the internet for exposed AI assistant ports and used an AI assistant to manage elements of the criminal infrastructure.
In one attack against an AI company, investigators found a lengthy intrusion chain that began with an unsecured AI imaging API. The attacker subsequently moved through credential decryption, recovered a JWT token, password cracking and a Kubernetes environment.
More than 6TB of data was stolen during that campaign, with the transfer still underway when researchers discovered it.
In another attack against a government-linked financial registry, the hacker reportedly stole more than 120,000 records before deleting the victim’s live production database.
CloudSEK believes Azazel may have Russian connections based on the use of fluent Russian in operational scripts and the Russian-language name assigned to a staging server.
The incident also reflects growing conflict between cybercriminal groups. Other ransomware gangs have recently fought over leak sites, stolen data and control of criminal infrastructure, showing that cooperation within the cybercrime ecosystem can quickly collapse when large amounts of money are involved.
Related Articles
Hackers Hijack Domains After Breaching Country-Code Registries and Obtain Rogue Certificates
Hackers Hijack Google-Related Domains After Compromising ccTLD Operators Hackers have hijacked domains...
South Korea Probes Bank Breaches Amid Suspected AI-Powered Cyberattacks
South Korea Investigates Bank Breaches as AI-Powered Hacking Is Suspected South Korean...
ClingSTUN Linux Backdoor Exploits Dozens of Vulnerabilities to Spread Across
Linux Backdoor ClingSTUN Uses STUN Protocol to Spread Across Vulnerable Devices A...


Pentagon Personnel Database Breach Exposes Sensitive Data of Millions
Pentagon Personnel Database Breach Exposes Sensitive Data of Millions The U.S. Department...

Leave a comment