




New P7 DarkSword iPhone Exploit Steals Crypto Data and Expands Remote Access
 scsecOctober 14, 20263 Mins read7
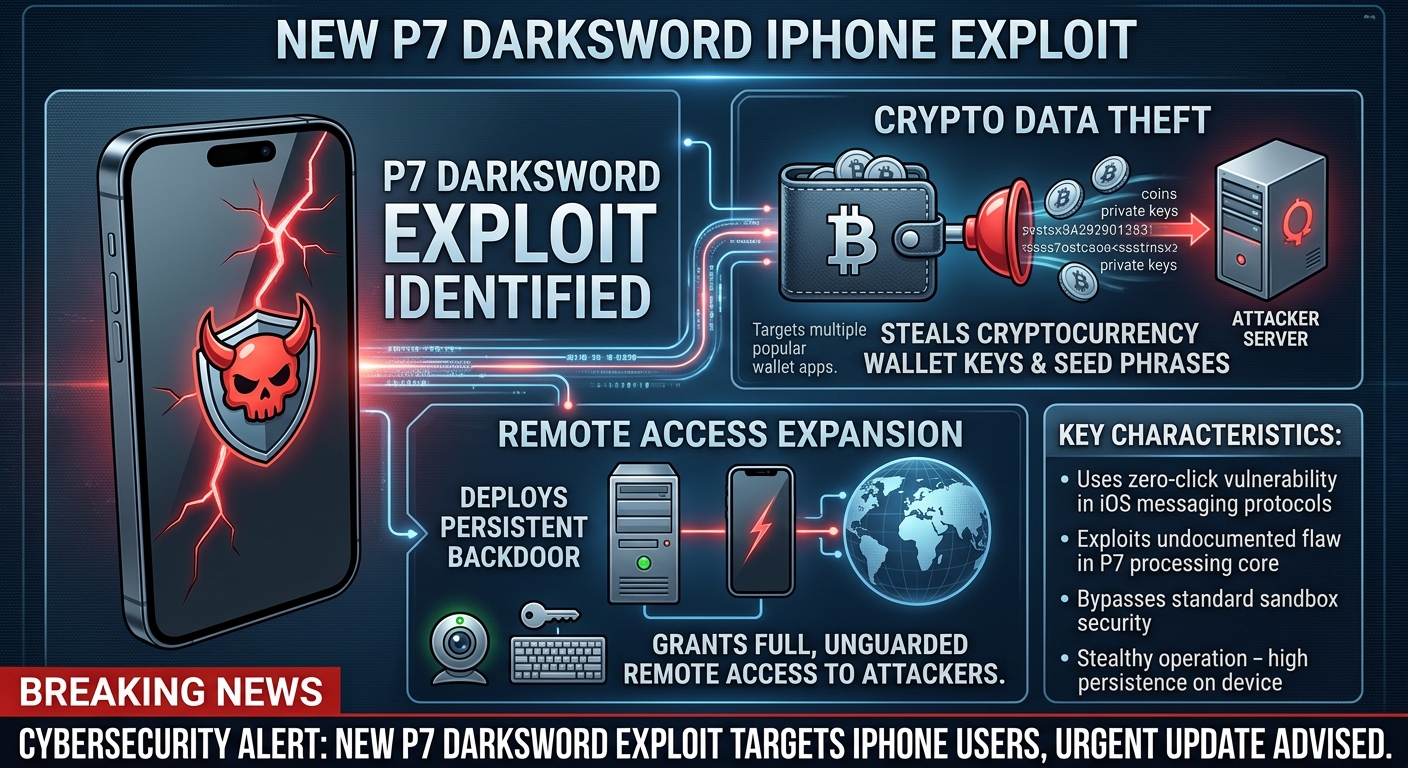
P7 DarkSword Exploit Kit Targets iPhones With Cryptocurrency Theft and Remote-Control Features
Cybersecurity researchers have identified a previously undocumented variant of the DarkSword iOS exploit kit that expands its ability to steal sensitive information from compromised iPhones.
The variant, known as P7 DarkSword, introduces additional capabilities for extracting cryptocurrency wallet information, accessing data stored in the iOS keychain, and communicating with attacker-controlled infrastructure.
According to research published by iVerify, the updated toolkit also reduces its footprint on infected devices, potentially making its activities more difficult to detect.
The discovery highlights the continuing evolution of mobile threats designed to compromise personal information and digital assets.
A More Advanced Version of DarkSword
DarkSword was publicly documented in March 2026 by researchers associated with Google’s Threat Intelligence Group, iVerify, and Lookout.
The earlier toolkit was designed to exploit multiple iOS vulnerabilities to compromise vulnerable devices.
P7 DarkSword represents a further development of that toolkit. Its name comes from the use of the variable prefix “p7_” in modifications made to the original code.
The updated version combines exploitation techniques with expanded data-theft and remote-management capabilities.
Exploiting Multiple iOS Vulnerabilities
The DarkSword toolkit uses chains of vulnerabilities to move beyond the restrictions normally imposed on browser processes.
Its exploitation process is designed to escape the browser sandbox, escalate privileges to the kernel level, and inject a primary payload into SpringBoard, an important component of the iOS interface.
Chaining vulnerabilities in this way can give attackers substantially greater access than a conventional malicious website would ordinarily possess.
The original toolkit was observed targeting iPhones running iOS versions between 18.4 and 18.7. Researchers reported that the toolkit had been detected in real-world activity in November 2025.
The precise exposure of an individual device depends on its software version, security updates, and the vulnerabilities used in a particular attack.
Cryptocurrency Wallet Data and Keychain Theft
One of the most significant additions in P7 DarkSword is its ability to target cryptocurrency-related information.
The variant can collect information from the iOS keychain, which stores certain sensitive credentials and other protected data, and target cryptocurrency wallet information available on the device.
This functionality creates additional risks for users who manage digital assets through their iPhones.
If attackers obtain sensitive wallet information or associated credentials, they may be able to use it in further attempts to access accounts or steal cryptocurrency.
The precise impact depends on what information is successfully extracted and the security protections surrounding each wallet.
Two-Way Communication With Attackers
P7 DarkSword also introduces two-way command-and-control communication with attacker-controlled infrastructure.
This capability allows the compromised device and the attacker’s systems to exchange information rather than relying solely on one-directional data transmission.
Combined with a smaller on-device footprint, this functionality could help attackers manage compromised devices while reducing the amount of persistent evidence left behind.
Remote communication can also support the delivery of instructions and the collection of stolen information.
The combination of exploitation, data theft, and remote control makes the variant a significant threat to vulnerable devices.
Why the Updated Toolkit Matters
The changes observed in P7 DarkSword illustrate how exploit kits can evolve beyond their original functionality.
Rather than focusing only on gaining access to an iPhone, the updated toolkit is equipped to pursue valuable information after a successful compromise.
Cryptocurrency wallet information is a particularly attractive target because stolen digital assets can be difficult to recover once unauthorized transactions have been completed.
The ability to collect keychain information also increases the potential consequences of an infection beyond a single application or service.
How iPhone Users Can Reduce Their Risk
Users should install the latest iOS security updates available for their devices and avoid visiting suspicious websites or following untrusted links.
Additional precautions include:
- Use a supported iPhone model that continues to receive security updates.
- Avoid installing applications or configuration profiles from untrusted sources.
- Enable available account protections, including multifactor authentication.
- Keep cryptocurrency wallet applications updated.
- Store recovery phrases securely and never enter them into suspicious websites or applications.
- Monitor cryptocurrency accounts for unexpected activity.
Security updates are especially important because exploit kits may rely on vulnerabilities that have already been addressed in newer software releases.
Conclusion
P7 DarkSword represents a concerning development in iOS exploitation, combining vulnerability chaining with cryptocurrency wallet data theft, keychain collection, and two-way remote communication.
Its reduced on-device footprint may complicate detection, while its expanded data-theft capabilities increase the potential consequences for affected users.
The discovery reinforces the need for timely security updates, cautious browsing, and strong protection of cryptocurrency credentials. iPhone users should not assume that mobile devices are immune to sophisticated attacks simply because they operate within a tightly controlled software ecosystem.




Related Articles

Tampered Ledger Signers Expose Hardware Wallet Supply-Chain Risks in $86 Million Crypto Heist
Hardware Implant in Ledger Devices Linked to Cryptocurrency Theft Exceeding $86 Million...

French Supermarkets Face Major Food Losses After Hackers Hijack Refrigeration Controllers
Cyberattack Forces French Supermarket Refrigerators to Heat Up to 50°C A cyberattack...

YMCO Network Leader Admits Role in Laundering Millions Through 15,000 Money Mules
Leader of International Money Mule Network Pleads Guilty in Major Cybercrime Laundering...


U.S. Authorities Take Down Flax Typhoon Domains Tied to Global Infrastructure Targeting
FBI Seizes Seven Domains to Disrupt China-Linked Flax Typhoon Cyber Operations The...

Leave a comment