FBI Links North Korea’s TraderTraitor to $6.43 Billion Binance Crypto Heist
 scsecNovember 8, 20261 Mins read0
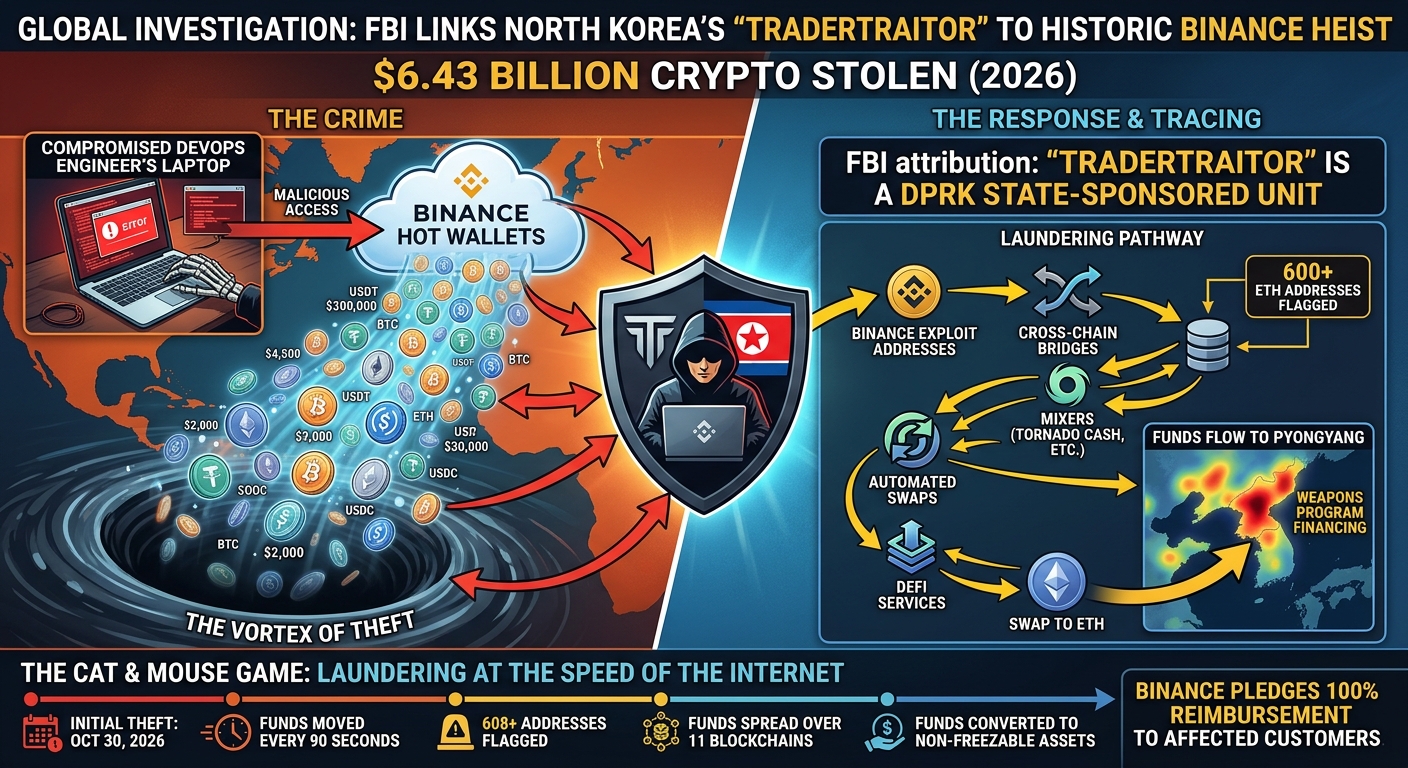
The US Federal Bureau of Investigation has officially attributed a massive cryptocurrency theft involving approximately $6.43 billion in digital assets to TraderTraitor, a hacking group linked to North Korea.
The group is also tracked by cybersecurity researchers under several other names, including Jade Sleet, Pressure Chollima, PUKCHONG, Slow Pisces, and UNC4899.
According to the FBI, the attackers stole cryptocurrency connected to Binance and subsequently began moving the funds through different blockchain networks. Investigators observed that much of the stolen cryptocurrency was being converted into Ethereum.
Authorities warned that the stolen assets could be moved through decentralized finance platforms and instant cryptocurrency exchange services to make financial tracking and recovery more difficult.
The FBI, US Secret Service, and Internal Revenue Service Criminal Investigation division are working together to investigate the incident and track the movement of the stolen funds.
Investigators also released cryptocurrency wallet addresses associated with the suspected laundering operation to help identify and monitor transactions.
The scale of the incident makes it one of the largest cryptocurrency thefts ever reported, surpassing the approximately $1.46 billion Bybit hack recorded in February 2025.
Blockchain security researchers reported that the stolen assets were spread across 11 blockchain networks, with approximately 82 percent associated with Ethereum and Bitcoin.
There has also been progress in freezing some of the stolen funds. According to the reported investigation, approximately $2.85 billion worth of assets had been frozen on-chain by companies including Tether, Circle, Ripple, Arbitrum, and Optimism.
Binance temporarily suspended certain withdrawal services following the incident but subsequently began restoring withdrawals in phases after conducting security assessments.
The investigation adds to growing concerns about North Korea-linked cybercriminal operations, which have increasingly targeted cryptocurrency platforms and financial infrastructure to generate funds.
Related Articles
APT29-Linked Hackers Hijack Web Analytics Script to Deliver iOS and Android Exploits create image
A cyber espionage campaign linked to the Russia-associated hacking group APT29 has...
mSecure Warns Users to Change Passwords and Reset 2FA After Suspicious Activity
Password manager provider mSecure has warned current and former customers to take...
Chinese Hackers Use ARTEX AI to Launch Automated Attacks Against More Than 200 Organizations
Chinese-linked hackers have reportedly used artificial intelligence-powered tools to conduct automated cyberattacks...


Iran-Linked DarkBlinders Hackers Target Israeli Individual and Iraqi Kurdish Government Cloud
Cybersecurity researchers have uncovered a cyber espionage campaign targeting an individual in...

Leave a comment