Iran-Linked DarkBlinders Hackers Target Israeli Individual and Iraqi Kurdish Government Cloud
 scsecNovember 8, 20261 Mins read0
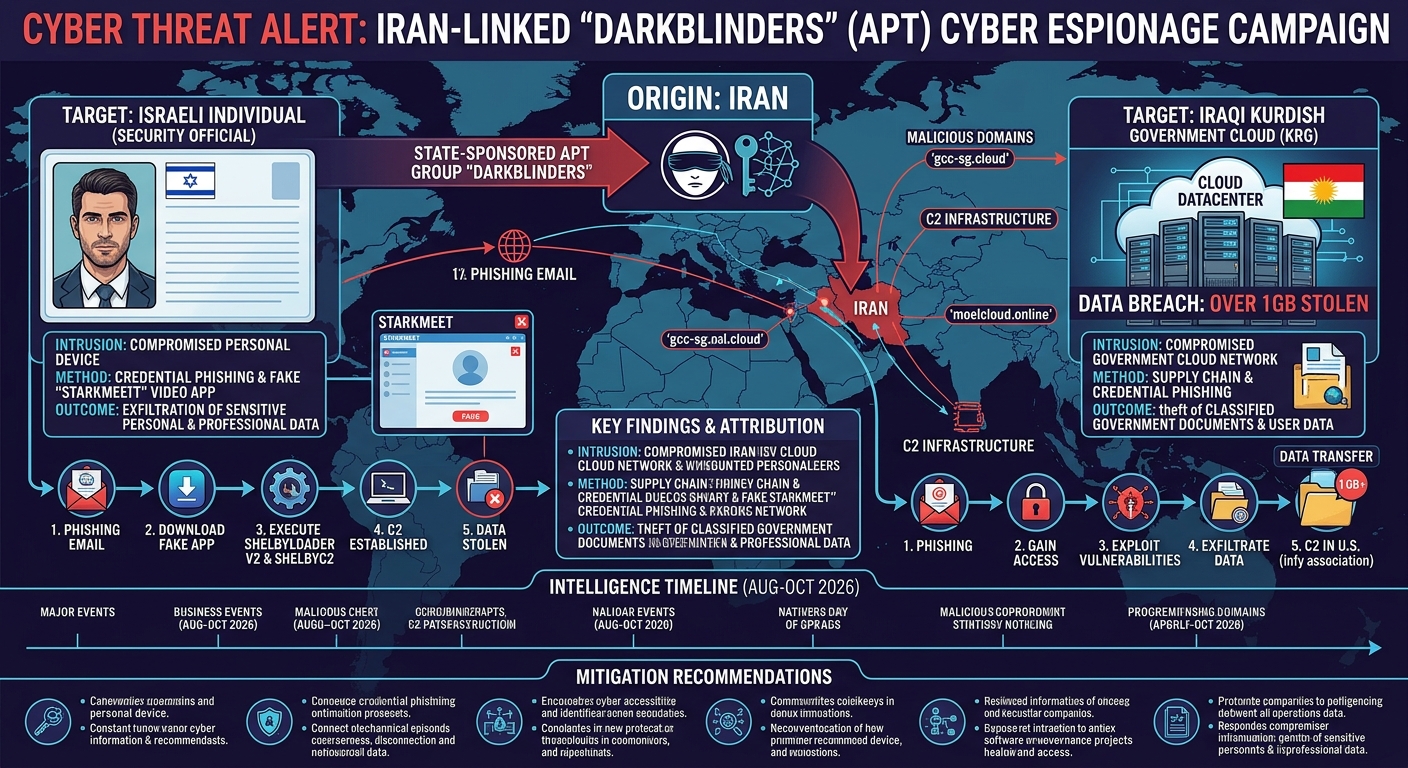
Cybersecurity researchers have uncovered a cyber espionage campaign targeting an individual in Israel and a government cloud environment in the Kurdistan Region of Iraq.
The operation reportedly took place between August and October 2026 and has been attributed to an Iran-aligned hacking group known as DarkBlinders.
According to researchers at Dream Research Labs, the campaign successfully compromised a high-profile individual in Israel and affected government cloud infrastructure in the Kurdistan Region.
DarkBlinders is believed to have been active since at least September 2024. The group has previously been associated with cyber operations targeting aviation infrastructure and telecommunications organizations in the United Arab Emirates and Iraq.
Investigators say the attackers frequently use spear-phishing techniques to gain initial access to targeted systems.
These attacks typically involve sending carefully prepared messages that encourage victims to download malicious software disguised as legitimate utilities or visit attacker-controlled websites.
Previous investigations have linked the group’s operations to malware families known as SHELBYLOADER and SHELBYC2.
The infection process can involve DLL sideloading, allowing malicious components to execute through seemingly legitimate software. Once deployed, the backdoor can provide attackers with remote access and capabilities for data theft.
Researchers have also identified connections between DarkBlinders activity and previous campaigns involving fake recruitment opportunities and malicious coding challenges.
In one earlier operation, attackers reportedly impersonated the IT department of Dubai Airports to distribute malware disguised as legitimate technical challenges.
The latest campaign highlights continuing cyber espionage concerns across the Middle East, particularly involving government infrastructure, telecommunications, and strategically important individuals.
Security experts warn that phishing remains an effective entry point for sophisticated hacking groups, making employee awareness and strong endpoint protection essential.
Related Articles
APT29-Linked Hackers Hijack Web Analytics Script to Deliver iOS and Android Exploits create image
A cyber espionage campaign linked to the Russia-associated hacking group APT29 has...
mSecure Warns Users to Change Passwords and Reset 2FA After Suspicious Activity
Password manager provider mSecure has warned current and former customers to take...
Chinese Hackers Use ARTEX AI to Launch Automated Attacks Against More Than 200 Organizations
Chinese-linked hackers have reportedly used artificial intelligence-powered tools to conduct automated cyberattacks...


Cyberattacks Hit More Than 40 European Supermarkets Through Refrigeration Systems
Supermarkets across several European countries have experienced suspected cyberattacks that remotely manipulated...

Leave a comment