Hackers Target Newly Discovered WordPress Vulnerability in Active Attacks
 scsecOctober 31, 20261 Mins read1
Hackers Begin Targeting Newly Disclosed WordPress Vulnerability
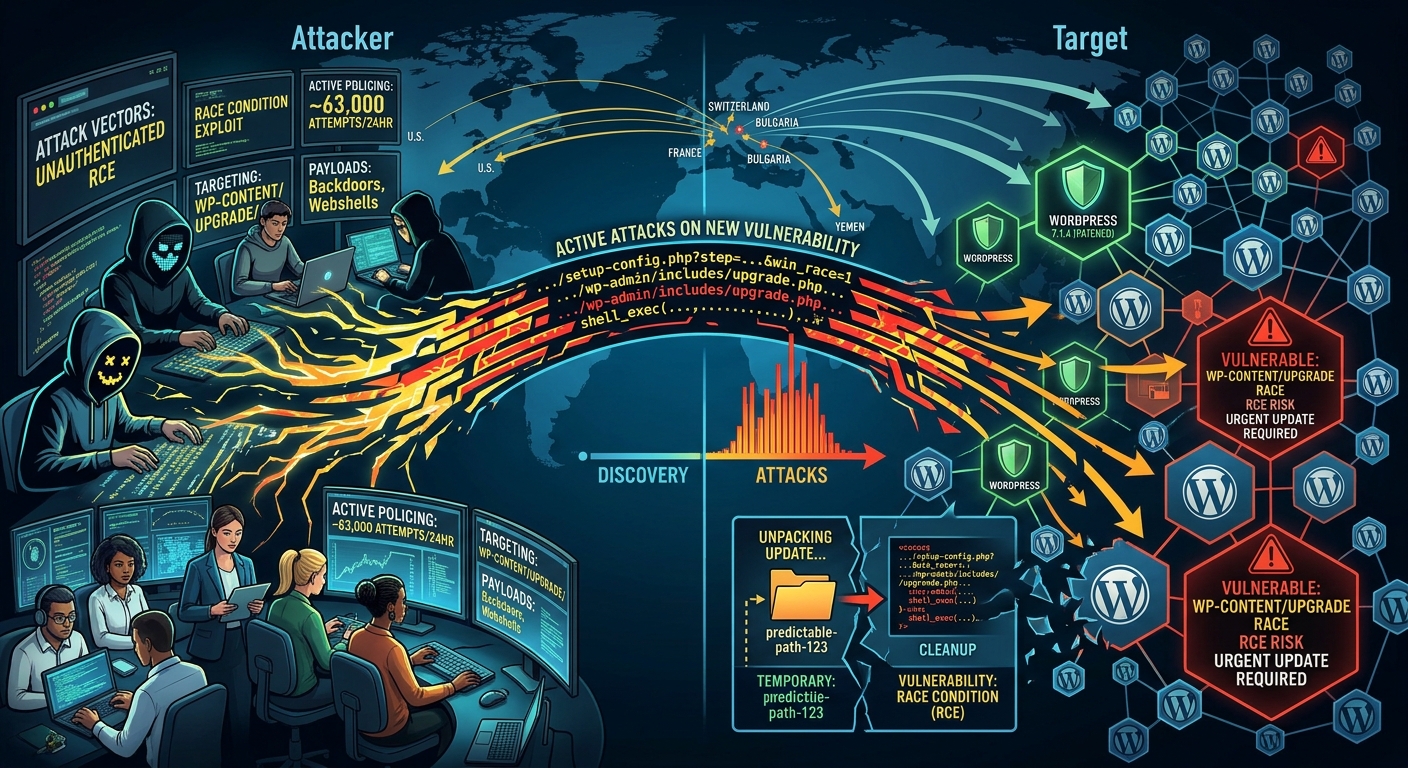
Cybersecurity researchers have reported active exploitation attempts targeting a newly discovered high-severity vulnerability in WordPress, increasing security concerns for website administrators and organizations relying on the popular content management platform.
The vulnerability involves a race condition in WordPress’s core update process and could potentially allow unauthenticated attackers to execute malicious code remotely under certain conditions.
The security issue is particularly concerning because attackers may exploit a narrow window during the website update process when temporary files and configuration data are being handled.
Researchers warned that predictable and publicly accessible staging directories could create opportunities for attackers to interfere with update operations and potentially execute unauthorized commands on vulnerable websites.
The flaw affects WordPress installations before the patched release, and security researchers have reported exploitation attempts shortly after the vulnerability became publicly known.
WordPress addressed the issue in version 7.1.4. Security fixes were also backported to supported older branches, extending protection to installations dating back to version 4.7.
The security update improves the protection of temporary staging directories by introducing randomized directory names, adding additional safeguards, and preventing unsafe promotion of staged configuration data.
Although the vulnerability requires specific conditions and exploitation involves a narrow timing window, a successful attack could result in serious consequences, including website compromise and unauthorized access to server resources.
Website administrators are strongly advised to update immediately to WordPress 7.1.4 or the appropriate patched release for their supported branch.
Organizations should also review server logs, monitor suspicious update activity, and ensure that temporary directories are not unnecessarily exposed to the internet.
The incident reinforces the importance of promptly installing security updates, particularly when vulnerabilities affect widely deployed website infrastructure.
Related Articles
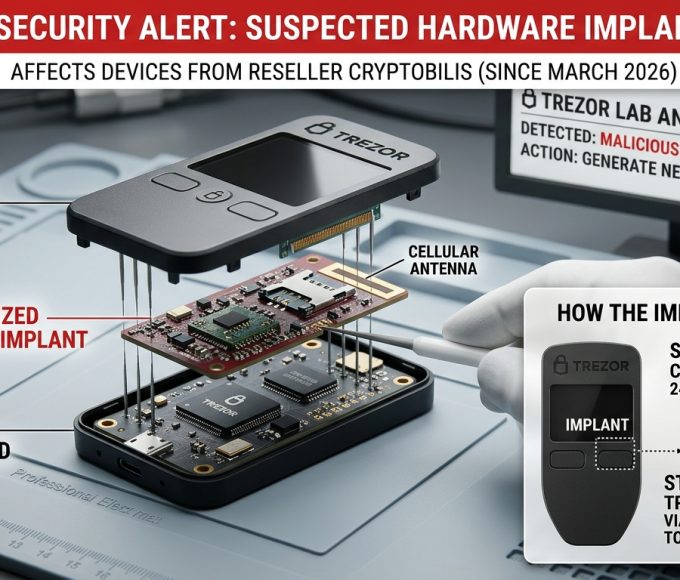
Trezor Warns of Suspected Crypto-Stealing Hardware Implant in Safe 5 Wallets
Trezor Warns of Suspected Cryptocurrency Theft Implant in Safe 5 Hardware Wallets...
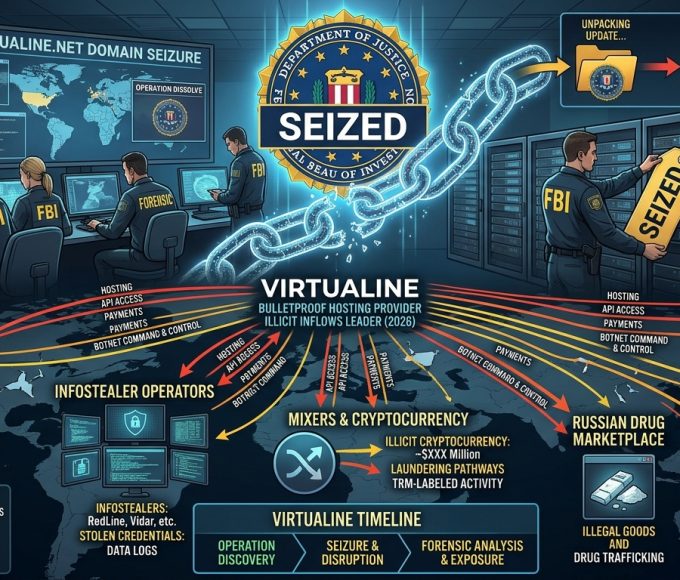
FBI Seizes Virtualine Domain Over Alleged Links to Cybercrime Networks
FBI Seizes Virtualine Domain Over Alleged Links to Major Cybercriminal Operations The...
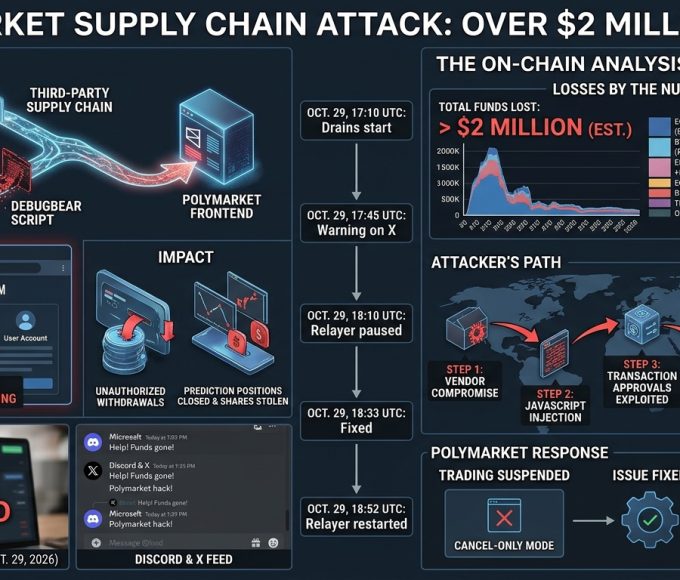
Polymarket Traders Lose Over $2 Million in Third-Party Supply Chain Attack
Polymarket Traders Lose More Than $2 Million in Third-Party Supply Chain Attack...
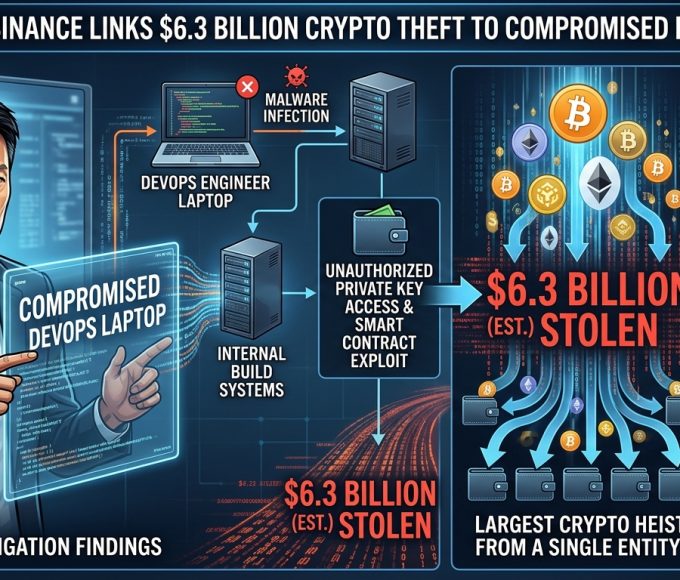


Binance Links $6.3 Billion Crypto Theft to Compromised DevOps Laptop
Binance Links $6.3 Billion Cryptocurrency Theft to Compromised DevOps Engineer’s Laptop Cryptocurrency...

Leave a comment