Researchers Use OpenAI AI Agents to Build a $250,000 Chrome Exploit in Six Days
 scsecOctober 19, 20262 Mins read4
Researchers Use OpenAI AI Agents to Build a $250,000 Chrome Exploit in Six Days
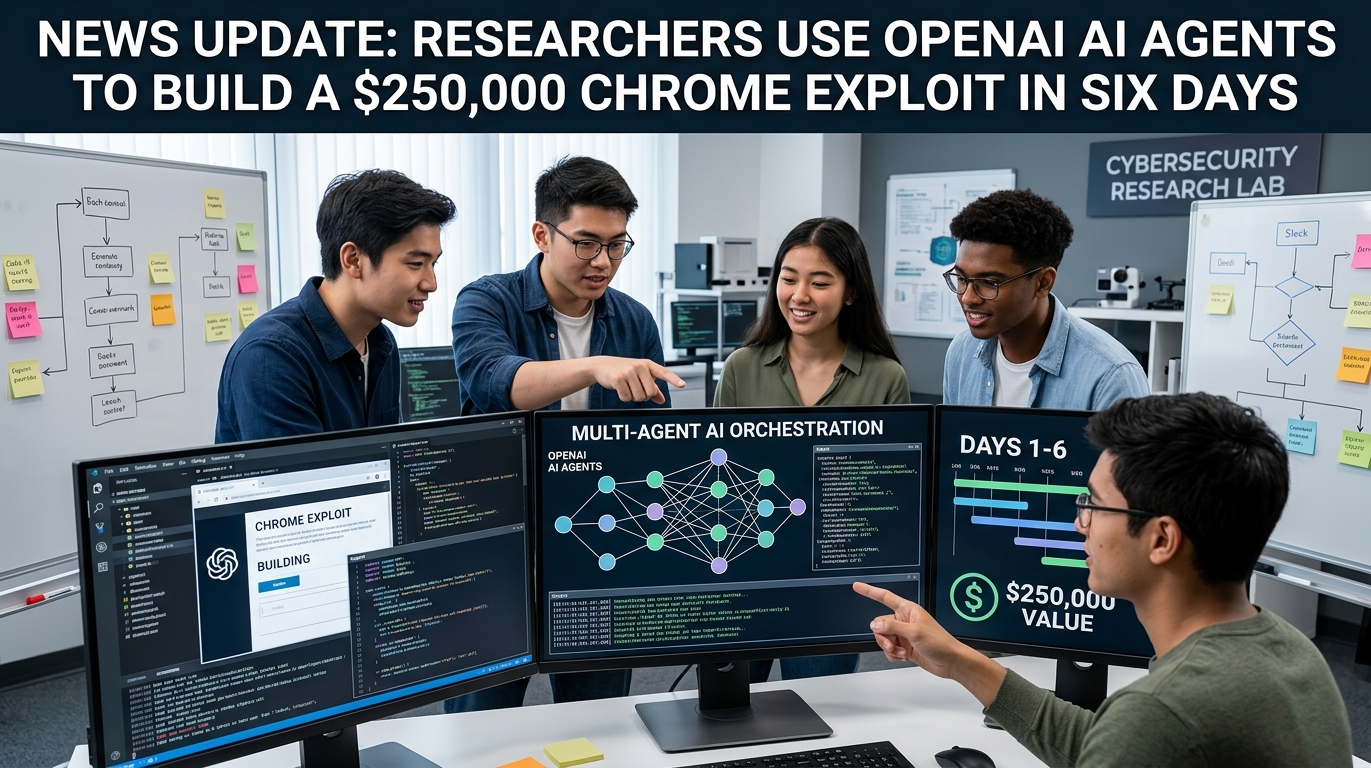
Security researchers have demonstrated how artificial intelligence can accelerate advanced vulnerability research after developing a sophisticated Google Chrome exploit in just six days.
The team at cybersecurity firm XBOW used AI agents powered by OpenAI’s publicly available GPT-5.6 Sol model to investigate and combine three previously unknown Chrome vulnerabilities into a single attack chain.
The resulting exploit could execute code on a Windows computer when a victim loaded a malicious webpage, without requiring a separate download or click.
Google confirmed the vulnerabilities, released fixes, and awarded XBOW its top $250,000 reward for a full Chrome exploit chain.
How Researchers Combined Three Vulnerabilities
Modern browsers use multiple security mechanisms to prevent malicious webpages from accessing the underlying operating system.
The researchers combined three weaknesses affecting different Chrome components to bypass these protections.
The vulnerabilities involved Chrome’s V8 JavaScript engine, its animated WebP image decoder, and the Crashpad crash-reporting component.
By chaining the weaknesses together, the researchers demonstrated how an initial browser compromise could be extended beyond the browser’s security boundaries to execute code on the Windows system.
The research highlights how separate vulnerabilities can become substantially more dangerous when combined into a complete attack.
AI Accelerated the Vulnerability Research Process
According to XBOW, AI agents helped investigate Chrome’s source code, explore potential weaknesses, test ideas, and develop proof-of-concept exploit components.
Human researchers still played an important role by selecting targets, providing context, evaluating the results, and deciding which vulnerabilities could be combined into a working chain.
The successful development sprint took place between August 2 and August 7, 2026, during the Black Hat and DEF CON security conferences in Las Vegas.
However, the six-day achievement followed months of earlier research. XBOW said its first complete Chrome exploit chain had taken approximately two months to develop.
The team also encountered setbacks, including an early vulnerability that turned out to be known to Google. The researchers replaced that component and continued working toward a complete exploit.
XBOW estimated that the six-day effort consumed approximately $40,000 in AI-related computing costs.
Google Awards $250,000 for the Discovery
Google awarded XBOW $250,000 under its Chrome vulnerability reward program for the full exploit chain.
The discovery demonstrated how researchers could combine multiple weaknesses to overcome browser security protections that are designed to prevent malicious webpages from reaching the operating system.
Two of the vulnerabilities received public identifiers: CVE-2026-85045 and CVE-2026-78952. The image-decoder vulnerability was also addressed as part of the security fixes.
Google subsequently released updates addressing all three issues.
Why AI-Assisted Exploit Development Matters
Developing a complete browser exploit traditionally requires substantial technical expertise and considerable time.
AI-assisted research may reduce the effort needed to examine large codebases, explore possible vulnerabilities, and test different approaches.
This can benefit defensive security teams by helping them identify weaknesses before attackers discover them.
However, the same capabilities could potentially help malicious actors develop sophisticated exploits more quickly, reducing the time organizations have to respond to newly discovered vulnerabilities.
What Chrome Users Should Do
Users should keep Google Chrome updated and restart the browser after installing security updates.
Organizations should also establish reliable browser-patching procedures, prioritize security fixes, and monitor vulnerability disclosures affecting software used across their environments.
Security teams should pay particular attention to internet-facing applications and systems that depend on browser automation.
Conclusion
The XBOW demonstration highlights the growing role of AI in advanced cybersecurity research.
By combining AI-assisted analysis with human expertise, researchers developed a sophisticated Chrome exploit chain in six days and received a $250,000 reward.
Although Google has fixed the reported vulnerabilities, the case illustrates why rapid security testing and timely patching are becoming increasingly important as AI tools accelerate vulnerability discovery.
Related Articles
Israeli Advertising Agency Linked to Zero-Click Spyware Campaign
Israeli Advertising Agency Linked to Zero-Click Spyware Campaign An Israeli digital advertising...
UK Legal Aid Agency Data Breach Exposes Records Dating Back to 1978
UK Legal Aid Agency Data Breach Exposes Records Dating Back to 1978...
Nearly Half of Businesses Report Unauthorized AI Agent Activity
Nearly Half of Businesses Report Unauthorized AI Agent Activity Artificial intelligence agents...


FBI Shuts Down 40 Laptop Farms in $3 Million North Korean Employment Fraud Scheme
FBI Shuts Down 40 Laptop Farms in $3 Million North Korean Employment...

Leave a comment