FBI Seizes Virtualine Domain Over Alleged Links to Cybercrime Networks
 scsecOctober 31, 20261 Mins read0
FBI Seizes Virtualine Domain Over Alleged Links to Major Cybercriminal Operations
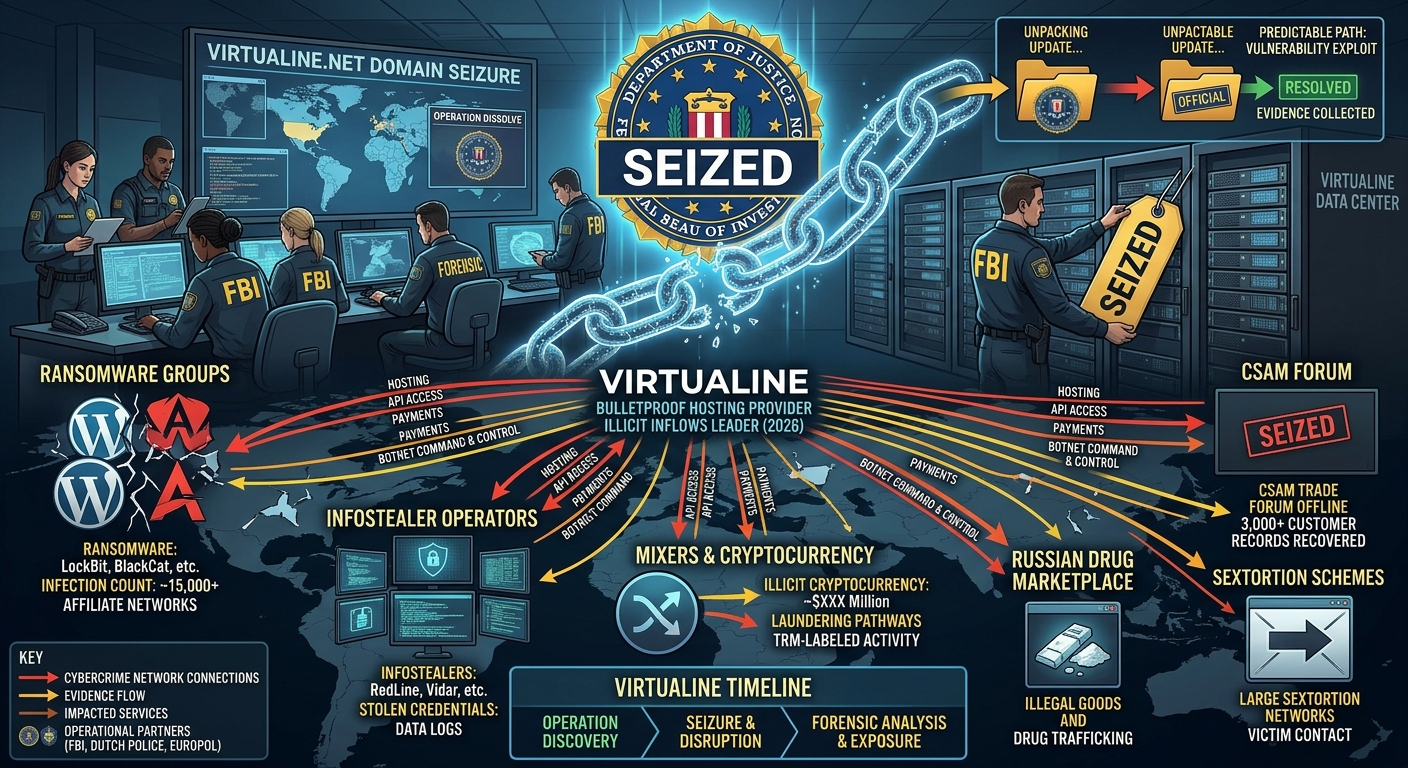
The FBI has seized the primary domain of Virtualine, a Russian-speaking bulletproof hosting provider accused of supporting cybercriminal operations and helping malicious customers evade law enforcement investigations.
The seized domain, virtualine.net, was associated with a hosting service that allegedly provided infrastructure for phishing campaigns, spam operations, ransomware activities, information-stealing malware, and other illegal services.
According to court documents, Virtualine also operated under several alternative names, including Secury, Massgod, Spamhouse, Lanedo, and Omegatech.
The provider reportedly advertised its ability to protect customers from abuse complaints and law enforcement requests. It also promoted services designed to move customer infrastructure to alternative hosting environments when existing servers faced disruption.
Investigators alleged that the company continued supporting customers involved in illegal activities despite receiving numerous complaints and takedown requests from authorities in multiple countries.
One particularly serious allegation involved hosting services connected to websites distributing sexually explicit material involving minors. Authorities also linked the provider to a hack-for-hire operation targeting online accounts to steal private content.
According to blockchain intelligence company TRM Labs, Virtualine received cryptocurrency payments from several criminal sources and was associated with ransomware operators and information-stealing malware distributors.
Analysis of cryptocurrency transactions linked to the hosting provider showed that a significant proportion of payments originated from a Russian drug marketplace, sextortion operations, cryptocurrency mixing services, and ransomware-related activities.
The provider reportedly emerged on the cybercrime forum Exploit in 2024, although it claimed to have been operating since 2019.
Investigators also identified connections between Virtualine and the StealC information-stealing malware operators during 2026.
The FBI’s domain seizure represents an important disruption to the provider’s online operations. However, cybersecurity analysts caution that taking control of a domain does not necessarily eliminate the underlying hosting infrastructure or prevent operators from establishing replacement services.
Authorities continue examining the provider’s activities and its connections to criminal networks.
The case demonstrates how bulletproof hosting services can become an important part of the cybercrime ecosystem by providing infrastructure that allows malicious actors to maintain operations despite repeated law enforcement intervention.
Related Articles
Trezor Warns of Suspected Crypto-Stealing Hardware Implant in Safe 5 Wallets
Trezor Warns of Suspected Cryptocurrency Theft Implant in Safe 5 Hardware Wallets...
Hackers Target Newly Discovered WordPress Vulnerability in Active Attacks
Hackers Begin Targeting Newly Disclosed WordPress Vulnerability Cybersecurity researchers have reported active...
Polymarket Traders Lose Over $2 Million in Third-Party Supply Chain Attack
Polymarket Traders Lose More Than $2 Million in Third-Party Supply Chain Attack...


Binance Links $6.3 Billion Crypto Theft to Compromised DevOps Laptop
Binance Links $6.3 Billion Cryptocurrency Theft to Compromised DevOps Engineer’s Laptop Cryptocurrency...

Leave a comment