Trezor Warns of Suspected Crypto-Stealing Hardware Implant in Safe 5 Wallets
 scsecOctober 31, 20262 Mins read0
Trezor Warns of Suspected Cryptocurrency Theft Implant in Safe 5 Hardware Wallets
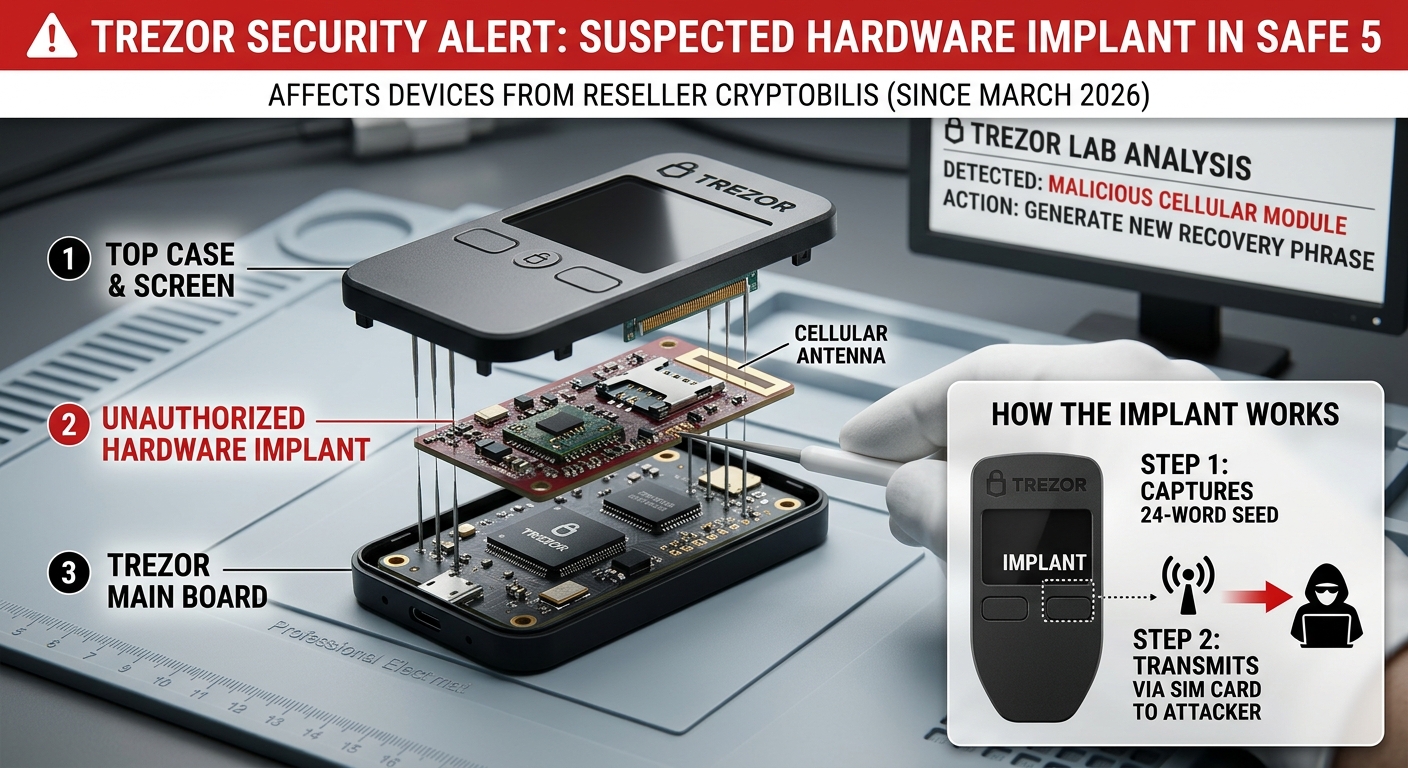
Cryptocurrency hardware wallet manufacturer Trezor has warned customers about a suspected malicious hardware implant discovered in a Trezor Safe 5 device purchased through a Southeast Asian reseller.
The company received a report from an Indonesian customer who purchased the device through CryptoBilis on the Tokopedia marketplace in August 2026.
After opening the hardware wallet, the customer reportedly discovered an additional circuit board positioned between the device’s main circuit board and its screen.
The suspicious component allegedly contained a cellular communication module and an antenna, raising concerns that the device had been modified to secretly capture sensitive cryptocurrency information.
According to the customer’s initial findings, the implant may be capable of reading information displayed on the device’s screen, including the wallet recovery phrase, and transmitting the captured information through a mobile network.
A recovery phrase is particularly sensitive because anyone who obtains it may gain access to the cryptocurrency stored in the associated wallet.
Trezor described the report as credible but emphasized that it has not yet physically examined the device. The company is waiting to receive the suspected compromised hardware before confirming the implant’s functionality.
The incident follows a similar supply chain security problem involving Ledger hardware wallets sold through the same reseller. That earlier incident prompted Ledger to investigate potentially compromised devices and ask distributors in Southeast Asia and Hong Kong to temporarily halt sales.
Trezor had already stopped selling devices through CryptoBilis on October 9, 2026, after learning about the earlier Ledger incident.
The company has also announced plans to restructure and strengthen its global reseller network to improve supply chain security.
Trezor stated that it is currently unaware of any cryptocurrency theft directly resulting from the suspected implant and promised to provide further information after examining the device.
For precautionary reasons, the company recommends that customers avoid setting up or using Trezor devices purchased through CryptoBilis from March 2026 onward.
Customers who have already used potentially affected devices should immediately transfer their cryptocurrency to a newly created wallet using a completely new recovery phrase.
Users with valid proof of purchase may contact Trezor to request a replacement device or a voucher for another wallet.
The company also warned that weighing a hardware wallet is not a reliable method of identifying malicious modifications.
The incident highlights the growing risks of hardware supply chain attacks, demonstrating that even physical cryptocurrency security devices can be manipulated before reaching customers.
Related Articles
FBI Seizes Virtualine Domain Over Alleged Links to Cybercrime Networks
FBI Seizes Virtualine Domain Over Alleged Links to Major Cybercriminal Operations The...
Hackers Target Newly Discovered WordPress Vulnerability in Active Attacks
Hackers Begin Targeting Newly Disclosed WordPress Vulnerability Cybersecurity researchers have reported active...
Polymarket Traders Lose Over $2 Million in Third-Party Supply Chain Attack
Polymarket Traders Lose More Than $2 Million in Third-Party Supply Chain Attack...


Binance Links $6.3 Billion Crypto Theft to Compromised DevOps Laptop
Binance Links $6.3 Billion Cryptocurrency Theft to Compromised DevOps Engineer’s Laptop Cryptocurrency...

Leave a comment