Israeli Advertising Agency Linked to Zero-Click Spyware Campaign
 scsecOctober 19, 20263 Mins read3
Israeli Advertising Agency Linked to Zero-Click Spyware Campaign
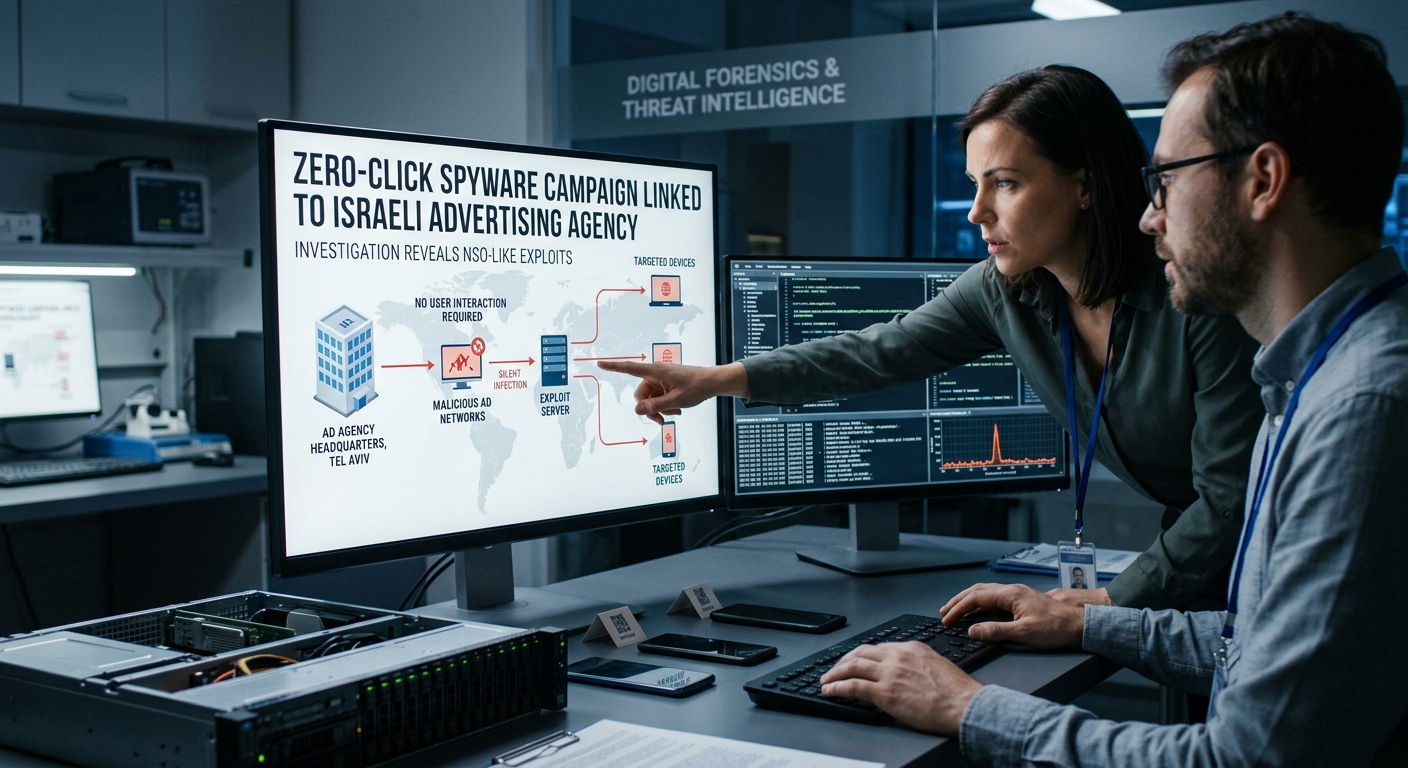
An Israeli digital advertising company has been linked to a surveillance operation that allegedly used online advertisements to deliver spyware to mobile devices without requiring users to click on anything.
The company, Discover-Tech, was investigated by Citizen Lab over its Controlium advertising platform, which researchers said was used to identify potential targets and deliver malicious advertising associated with a technique known as AdFection.
The investigation described the activity as the first documented instance of mercenary spyware being delivered through targeted advertisements in real-world operations without requiring user interaction.
The findings raise concerns about the potential misuse of advertising technology and the security of applications that display third-party advertisements.
How the Zero-Click Attack Worked
Traditional cyberattacks often rely on victims clicking malicious links, downloading files, or installing harmful applications.
Zero-click attacks are different because they may succeed without requiring a deliberate action from the target.
According to the investigation, the AdFection technique used targeted advertising infrastructure to identify potential victims and deliver malicious content through advertisements.
The process allegedly involved profiling users, attempting to identify their devices, and serving advertisements containing JavaScript designed to exploit software vulnerabilities.
If the exploit succeeded, the attack could compromise a device without the user knowingly opening a suspicious link or downloading an application.
This approach makes zero-click attacks particularly concerning because users may have little indication that an infection attempt has occurred.
Popular Applications Appeared in the Advertising Network
Researchers identified Discover-Tech advertisements appearing in applications and services including Duolingo, Truecaller, Viber, Yahoo Mail, dating applications, period-tracking tools, and weather applications.
The appearance of an advertisement in an application does not automatically mean the application’s developer participated in the spyware operation or that every user was infected.
However, the findings demonstrate how advertising infrastructure can potentially become a delivery channel for sophisticated surveillance tools.
Because advertising networks distribute content across numerous applications and websites, malicious advertising can potentially reach a broad audience before the activity is detected.
Journalists and Sensitive Organizations Were Among the Targets
Citizen Lab reported that the spyware had been used against dozens of devices belonging to journalists who covered sensitive subjects at Al Jazeera.
The investigation also identified Discover-Tech advertisements in networks associated with the Pentagon, the International Atomic Energy Agency, and the International Criminal Court.
Media organizations and networks across several countries were also connected to the investigation.
These findings suggest that the operation had an international reach, although the presence of advertisements in a network does not establish that every connected device was compromised.
The reported targeting of journalists raises particular concerns about confidential communications, source protection, and the safety of individuals working on sensitive investigations.
Links to Commercial Spyware Companies
Researchers linked the Controlium platform to companies associated with commercial surveillance and spyware technology, including Candiru, Bindecy, and Intelos.
The investigation suggested that Discover-Tech’s advertising infrastructure may have connected conventional advertising systems with companies involved in targeted surveillance.
This raises questions about how technologies originally developed for audience targeting and advertising measurement can be repurposed for cyber espionage.
The findings also demonstrate the importance of examining relationships between advertising vendors, their customers, and the technologies used to deliver content.
Advertising Industry Oversight Comes Under Scrutiny
The investigation found that Discover-Tech had appeared on certified advertising vendor lists maintained by Google and IAB Europe.
Researchers questioned whether the industry’s existing verification and monitoring procedures were sufficient to identify potentially abusive companies.
Following the findings, Google and IAB Europe removed Discover-Tech from their respective advertising vendor lists.
The case highlights the limitations of relying on vendor certification alone. Advertising platforms need ongoing monitoring and effective procedures for identifying suspicious activity, investigating complaints, and removing malicious participants.
How Users and Businesses Can Reduce Risk
Although individual users cannot control every advertising network, they can reduce exposure by keeping operating systems and applications updated and removing software they no longer need.
People at elevated risk of targeted surveillance, including journalists and public officials, should consider specialized device-security guidance.
Organizations should also assess the security of applications used by employees and establish procedures for responding to suspected spyware infections.
Advertising platforms, meanwhile, should strengthen vendor verification, monitor unusual advertising behavior, and improve transparency around security investigations.
Conclusion
The Discover-Tech investigation highlights a troubling intersection between digital advertising and commercial spyware.
By allegedly using targeted advertisements to deliver zero-click exploits, the operation demonstrated how trusted online distribution channels could be repurposed for surveillance.
The company’s removal from major advertising vendor lists represents an important response, but the wider challenge remains: advertising ecosystems require stronger oversight to prevent malicious actors from exploiting legitimate technology infrastructure.
Related Articles
UK Legal Aid Agency Data Breach Exposes Records Dating Back to 1978
UK Legal Aid Agency Data Breach Exposes Records Dating Back to 1978...
Researchers Use OpenAI AI Agents to Build a $250,000 Chrome Exploit in Six Days
Researchers Use OpenAI AI Agents to Build a $250,000 Chrome Exploit in...
Nearly Half of Businesses Report Unauthorized AI Agent Activity
Nearly Half of Businesses Report Unauthorized AI Agent Activity Artificial intelligence agents...


FBI Shuts Down 40 Laptop Farms in $3 Million North Korean Employment Fraud Scheme
FBI Shuts Down 40 Laptop Farms in $3 Million North Korean Employment...

Leave a comment