Hackers Steal Up to $133 Million From French Bank Through Third-Party Service Provider
 scsecNovember 8, 20261 Mins read0
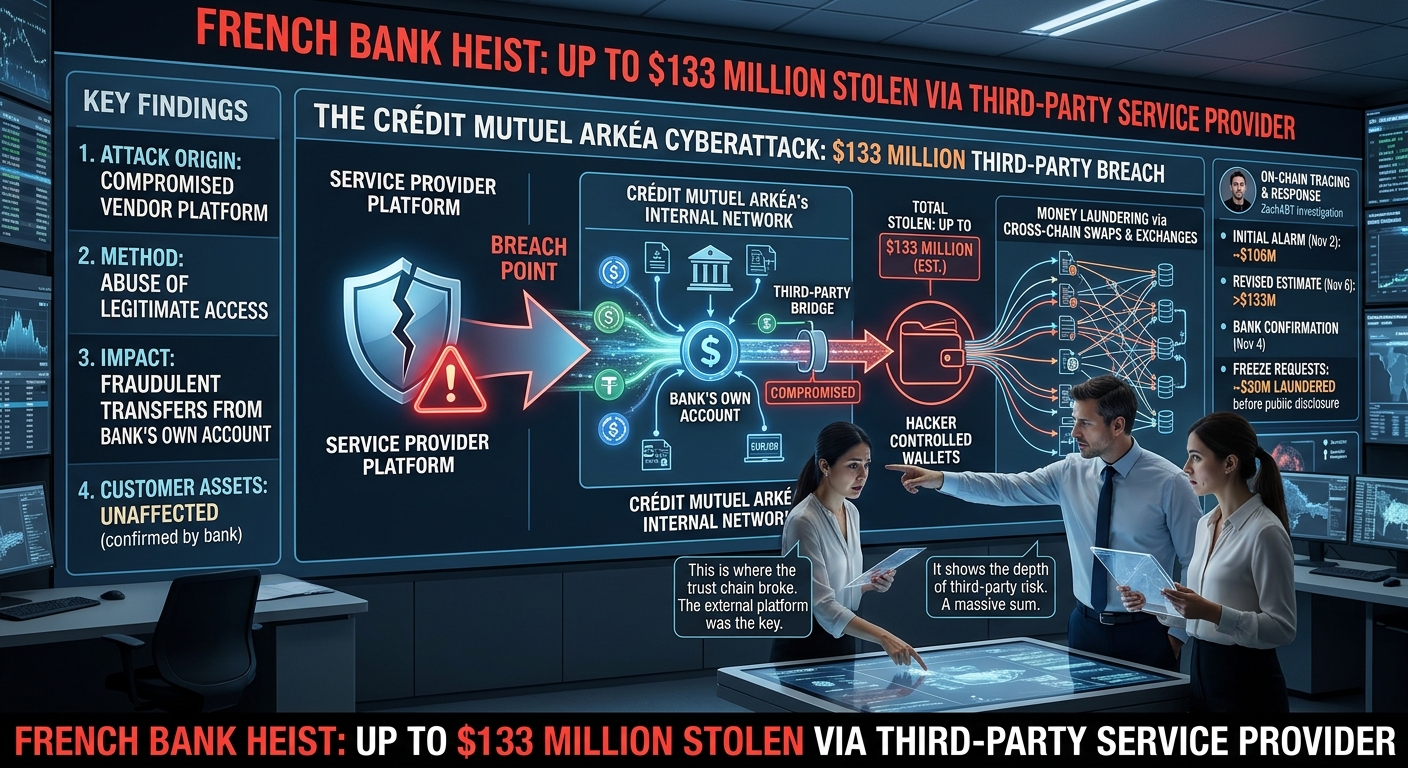
French banking group Crédit Mutuel Arkéa has suffered a major cyberattack that enabled attackers to initiate fraudulent financial transactions potentially worth up to $133 million.
The incident forced the bank to temporarily suspend certain systems while investigators worked to contain the attack and restore normal operations.
According to the bank, attackers gained access to its network through a platform operated by an external service provider.
Rather than directly accessing individual customer accounts, the attackers reportedly used the bank’s own account to initiate transactions involving other financial institutions.
Blockchain investigator ZachXBT first raised the alarm on November 2, reporting suspicious withdrawals involving multiple centralized cryptocurrency exchange accounts.
The investigator estimated that approximately 118 million euros, equivalent to around $133 million, may have been stolen.
The funds were reportedly converted into stablecoins, including USDC and USDT, before being moved through cryptocurrency networks.
ZachXBT also warned that approximately $30 million had potentially been laundered by November 3, raising concerns that delays in public disclosure could make it more difficult for authorities to freeze the stolen assets.
Crédit Mutuel Arkéa publicly acknowledged the incident on November 4 and stated that the situation was under control.
The bank reassured customers that their personal funds had not been affected. However, certain transfers experienced delays as the institution worked to secure its systems and restore normal banking operations.
The bank also confirmed that some stolen funds had been blocked but declined to verify the exact amount reported by the blockchain investigator.
In a separate explanation, the institution said the attackers had entered its network through a third-party service provider rather than through a direct compromise of customer accounts.
The incident is being investigated with the assistance of law enforcement and judicial authorities to establish the exact attack method and identify those responsible.
Following the breach, the bank warned customers about increased phishing risks and advised them not to share confidential information through unexpected emails or telephone calls.
Customers were encouraged to verify suspicious communications by contacting their banking advisers directly.
The incident demonstrates the serious cybersecurity risks associated with third-party service providers and highlights how weaknesses in external platforms can potentially expose major financial institutions to significant losses.
Related Articles
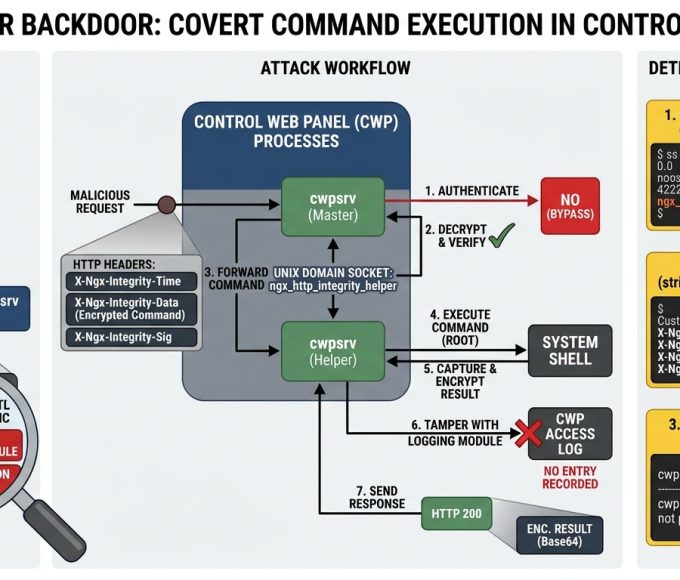
Hackers Hide Linux Backdoor in Control Web Panel to Execute Commands Without Logs
Cybersecurity researchers have discovered a previously identified backdoor hidden inside the web...
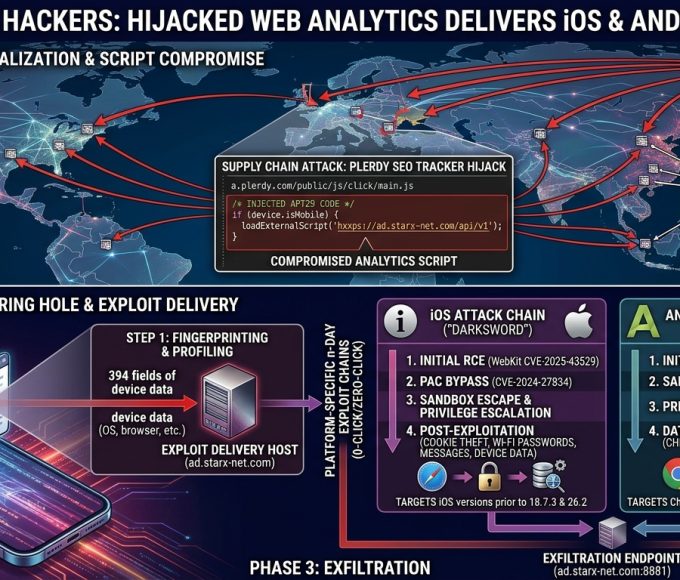
APT29-Linked Hackers Hijack Web Analytics Script to Deliver iOS and Android Exploits create image
A cyber espionage campaign linked to the Russia-associated hacking group APT29 has...
mSecure Warns Users to Change Passwords and Reset 2FA After Suspicious Activity
Password manager provider mSecure has warned current and former customers to take...


Chinese Hackers Use ARTEX AI to Launch Automated Attacks Against More Than 200 Organizations
Chinese-linked hackers have reportedly used artificial intelligence-powered tools to conduct automated cyberattacks...

Leave a comment