mSecure Warns Users to Change Passwords and Reset 2FA After Suspicious Activity
 scsecNovember 8, 20261 Mins read0
Password manager provider mSecure has warned current and former customers to take precautionary security measures following suspicious activity associated with its application.
In an email sent on November 3, 2026, the company, operated by mSeven Software, advised users to review their account security and consider changing passwords, resetting two-factor authentication methods, and removing stored passkeys.
The warning raised concerns among customers who use the application to store sensitive information, including login credentials and authentication details.
According to the email, mSeven had identified suspicious activity connected to the service and had launched an investigation with assistance from external cybersecurity specialists.
The company also stated that it had taken steps to contain the situation. However, the notification did not explain exactly what happened, which systems were affected, or whether customer vault information had been accessed.
The warning was reportedly sent to both current and former mSecure customers.
The incident is particularly concerning because mSecure allows users to store passwords, passkeys, and two-factor authentication codes in encrypted digital vaults.
Customers can synchronize their vault information through mSecure Cloud, Dropbox, iCloud, or Wi-Fi. However, the company did not clarify whether the suspicious activity affected any particular synchronization method.
mSecure has previously stated that customer vault information is encrypted on users’ devices before synchronization, meaning the company itself cannot normally access the stored information.
Nevertheless, the latest warning has encouraged users to take additional precautions while the investigation continues.
Customers should update passwords used for important accounts, review authentication settings, and remain alert for suspicious login attempts or unexpected security notifications.
The incident highlights the importance of transparency and rapid communication when security concerns affect services responsible for storing highly sensitive user information.
Related Articles
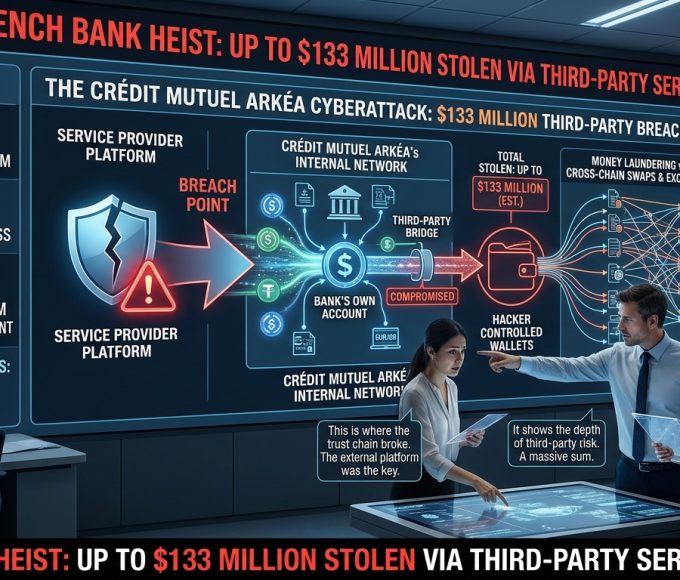
Hackers Steal Up to $133 Million From French Bank Through Third-Party Service Provider
French banking group Crédit Mutuel Arkéa has suffered a major cyberattack that...
Hackers Hide Linux Backdoor in Control Web Panel to Execute Commands Without Logs
Cybersecurity researchers have discovered a previously identified backdoor hidden inside the web...
APT29-Linked Hackers Hijack Web Analytics Script to Deliver iOS and Android Exploits create image
A cyber espionage campaign linked to the Russia-associated hacking group APT29 has...


Chinese Hackers Use ARTEX AI to Launch Automated Attacks Against More Than 200 Organizations
Chinese-linked hackers have reportedly used artificial intelligence-powered tools to conduct automated cyberattacks...

Leave a comment